New! PHP2Shell: Successful exploitation observed against a vulnerable GreyNoise sensor


Google Security Operations SOAR orchestrates security workflows to help teams investigate and respond to threats. GreyNoise adds real-time edge observability and context to SOAR workflows to enrich investigations and automate triage and response.
On-demand enrichment, pre-built playbooks, and webhooks for GreyNoise alerts and event feeds operationalize threat intelligence across four investigation and response use cases in Google Security Operations SOAR.
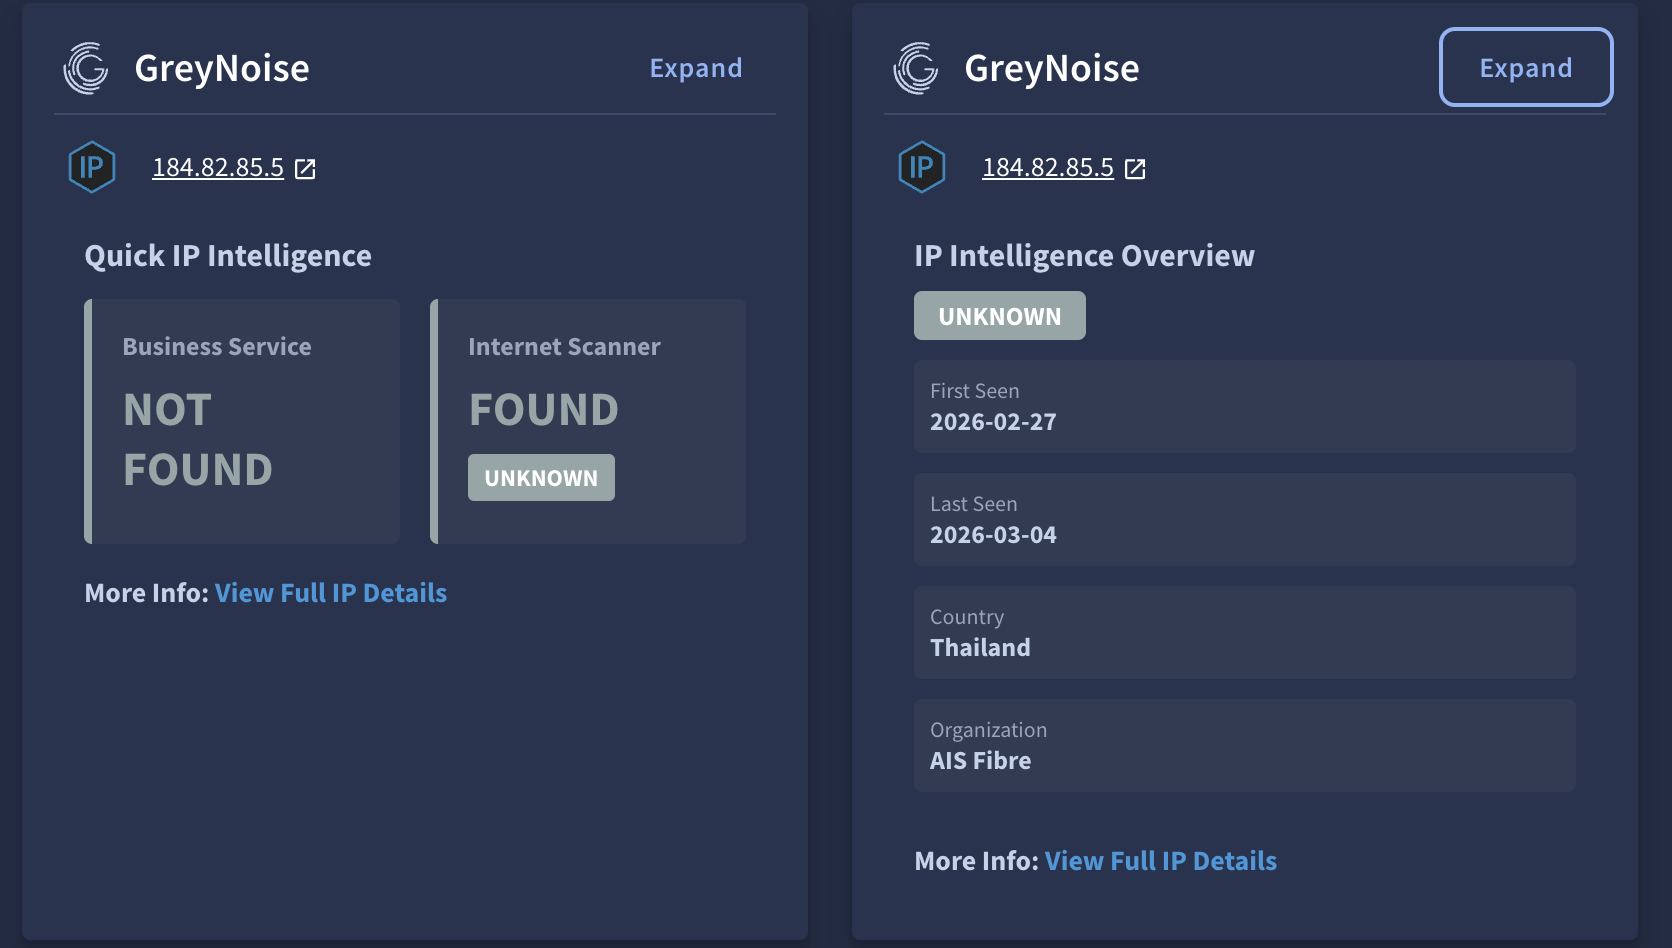
Many SOCs still rely on analysts to manually research IPs before determining whether an alert requires action. This repetitive process slows triage and leads to inconsistent decisions across the team.
Enrich IP-based alerts directly within Google Security Operations SOAR with GreyNoise data, including classification, tags, and threat level. Configured playbooks use GreyNoise lookup results to apply decision rules and modify cases based on the desired workflow. The enrichment appears in the Case Wall, giving analysts the context behind each triage decision.
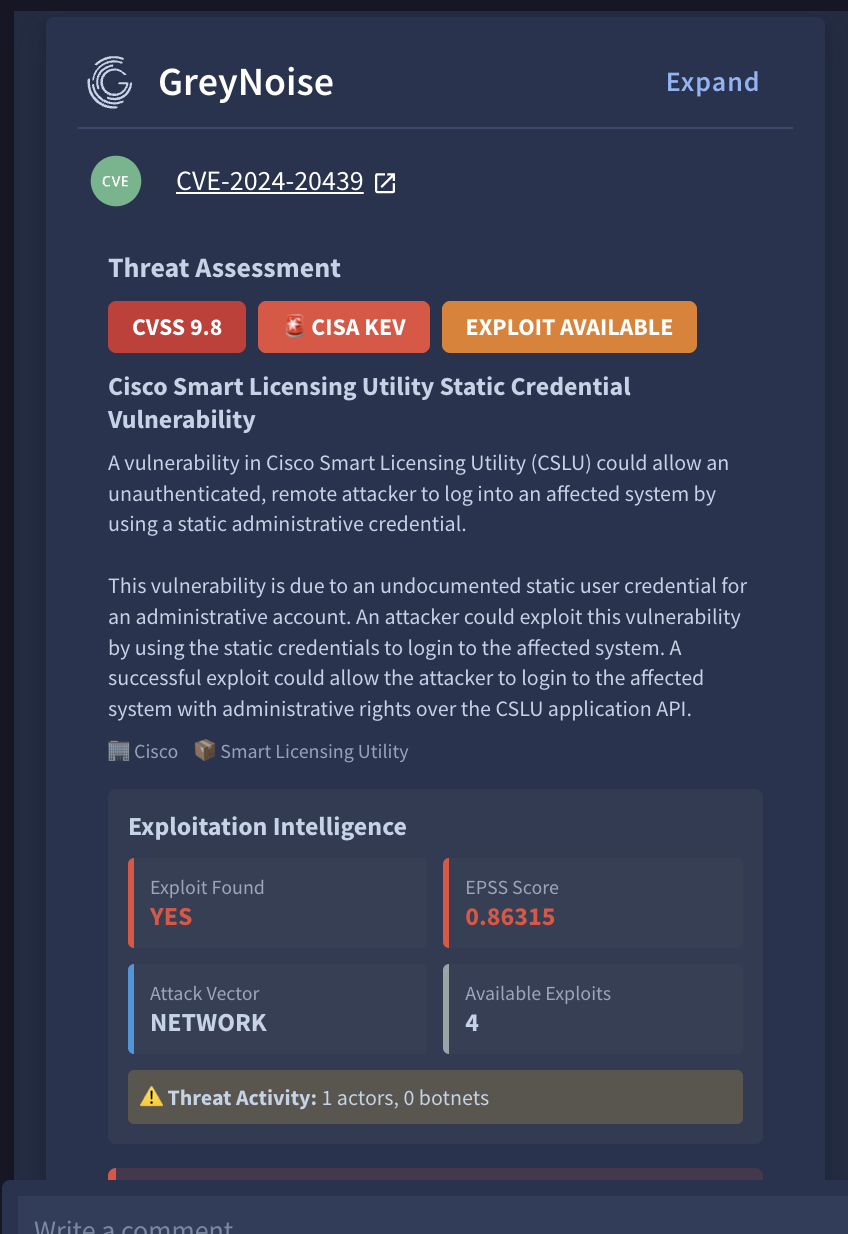
Individual organizations often cannot see exploitation patterns emerging across the internet. A sudden increase in scanning or exploitation against a vendor’s CVE can signal a zero-day or novel attack before the vendor publishes an advisory.
The pre-built CVE-Based Network Containment Orchestrator playbook responds when a GreyNoise webhook delivers a CVE activity spike or vendor CVE spike to Google Security Operations SOAR. It uses the CVE entity in the alert to identify the malicious IPs associated with that exploitation, enrich the case with actionable threat context, and initiate configured containment actions. Configure the relevant Event Feed in GreyNoise to control which CVE events are sent to Google Security Operations SOAR.
The result is early warning and automated containment, giving teams time to prioritize patching before attacks spread.
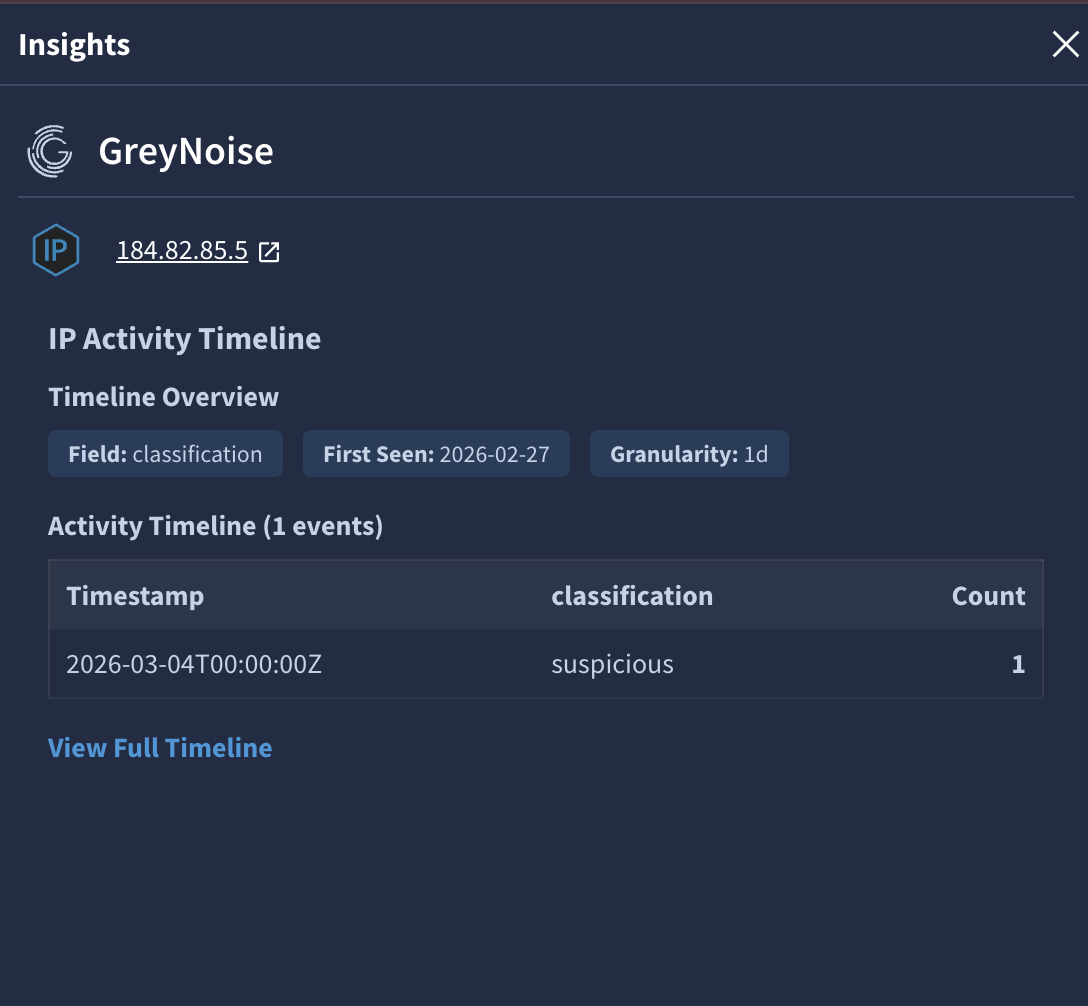
Compromised edge devices can scan the internet or communicate with attacker-controlled infrastructure undetected. Because many of these devices cannot run EDR agents, compromise may remain hidden until the activity is observed by external parties.
GreyNoise sends two high-confidence compromise signals into Google Security Operations SOAR. A webhook alerts when GreyNoise observes your public IP ranges conducting unsolicited scanning, while the callback IP feed identifies new attacker-controlled destinations for correlation with outbound traffic. Either signal triggers automatic case creation and a containment ticket, helping teams respond in seconds and track persistent issues in a single case timeline.
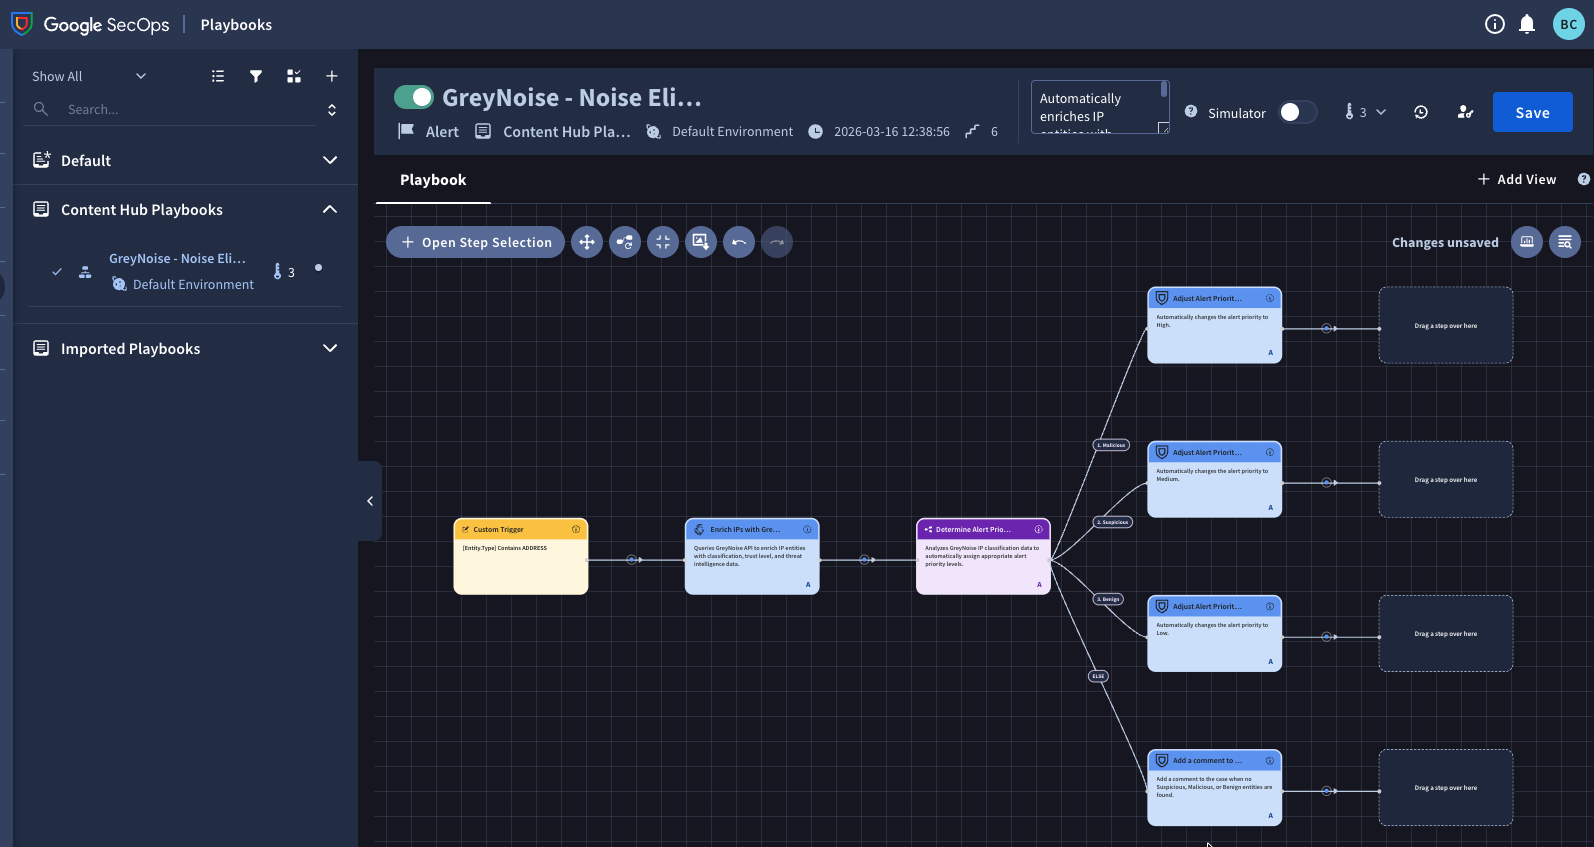
Automating blocklist updates can accelerate response, but blocking an IP associated with a legitimate business service can disrupt critical operations. Security teams need a reliable validation step before adding an IP to a blocklist.
Use GreyNoise Business Service Intelligence in Google Security Operations SOAR playbooks to validate IPs before adding them to a blocklist. Configured playbooks can route IPs associated with legitimate business services for analyst review, while network integrations block or unblock eligible IPs based on your response logic. This helps teams automate containment with greater confidence while reducing the risk of disrupting critical services.


