New! PHP2Shell: Successful exploitation observed against a vulnerable GreyNoise sensor


Google Security Operations SIEM brings security telemetry, detection, investigation, and response into one unified platform. GreyNoise adds real-time edge observability and context to help detect attacks on edge devices.
Pre-built dashboards, YARA-L detection rules, and saved searches operationalize four documented GreyNoise use cases in Google Security Operations SIEM.
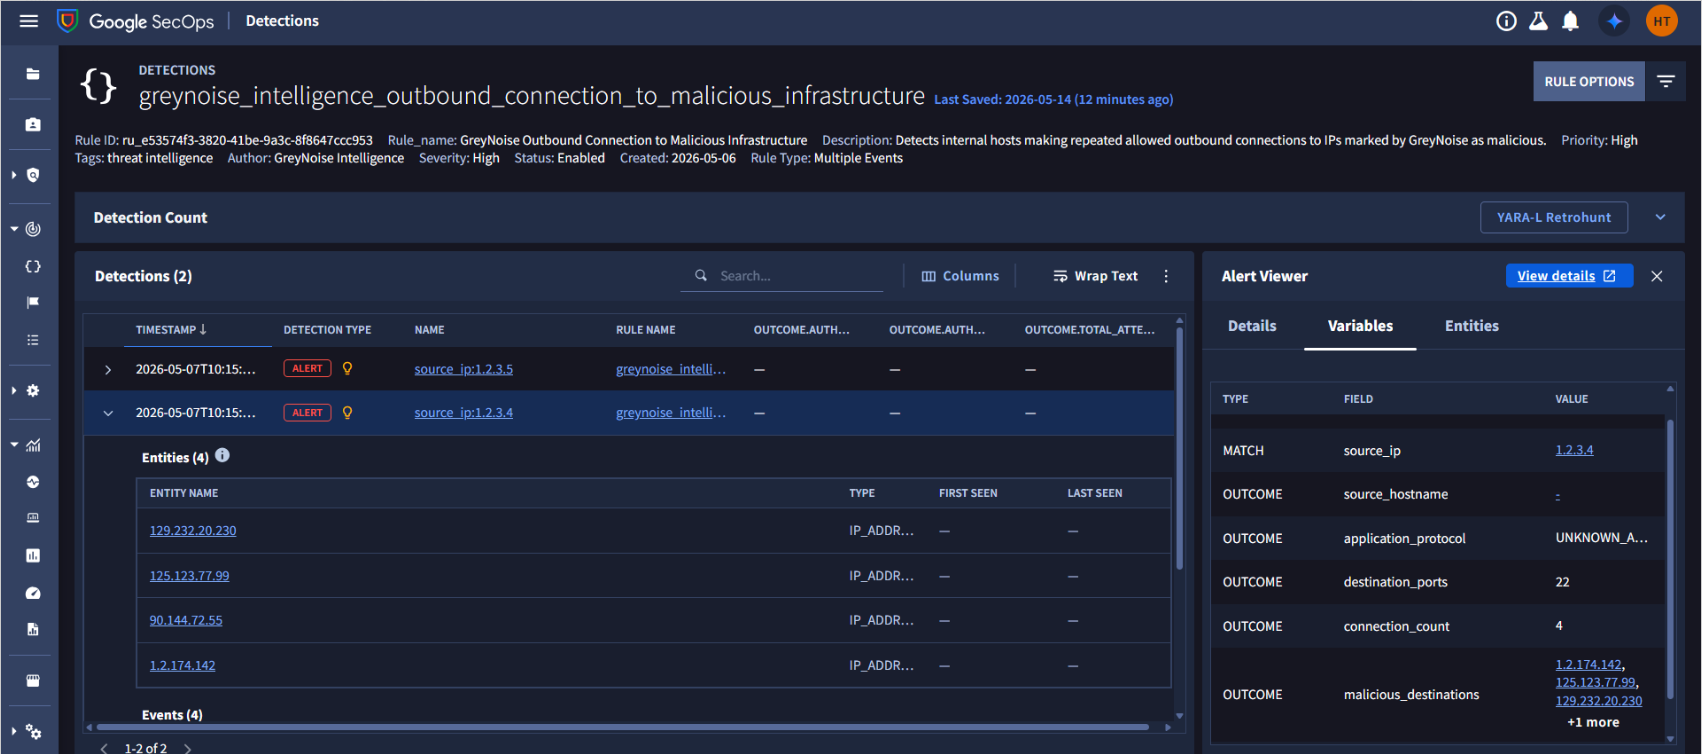
An internal host making repeated outbound connections to known malicious infrastructure is a strong indicator of compromise. It may signal command-and-control beaconing, data exfiltration, or botnet participation.
A purpose-built YARA-L detection rule correlates internal egress and outbound logs with infrastructure GreyNoise has observed and classified as malicious. Google Security Operations SIEM surfaces internal hosts that have successfully connected to known C2 servers, active exploitation infrastructure, or botnet staging grounds, giving analysts a high-fidelity signal for immediate investigation.
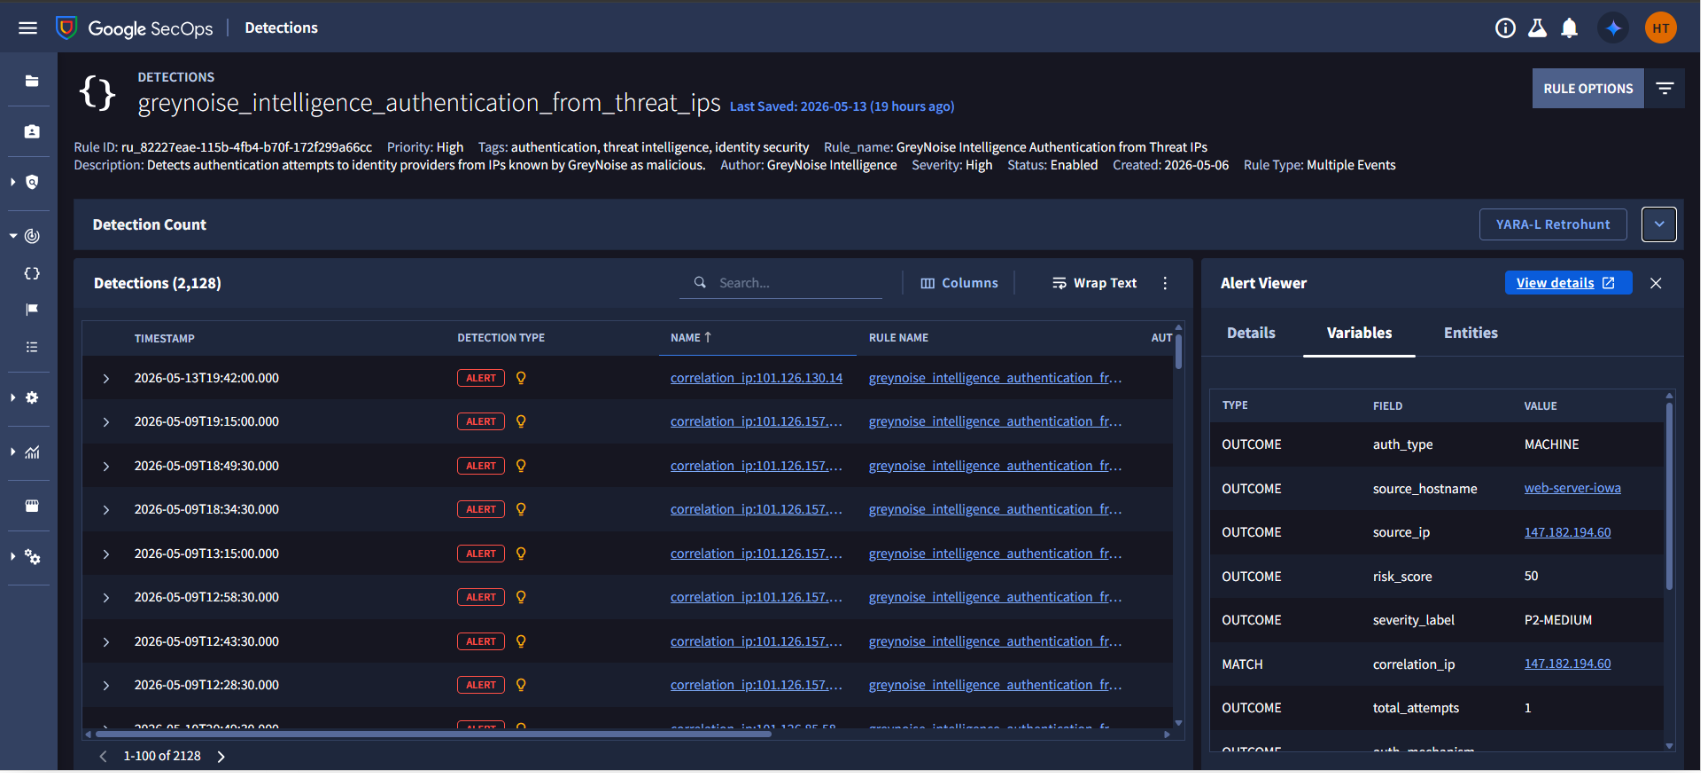
Authentication failures and brute-force attempts from the internet are constant for any perimeter device. The trouble is telling opportunistic account access apart from attempts aimed specifically at your organization. Hosts running mass scans or operating as part of botnet or proxy infrastructure authenticate to VPNs and identity providers all the time, and standard detection logic doesn’t flag it.
Google Security Operations SIEM correlates successful and failed authentication events with IPs GreyNoise classifies as malicious or suspicious. The YARA-L detection rule assigns risk and priority based on the GreyNoise verdict and authentication outcome, helping analysts identify successful compromises and active attempts.
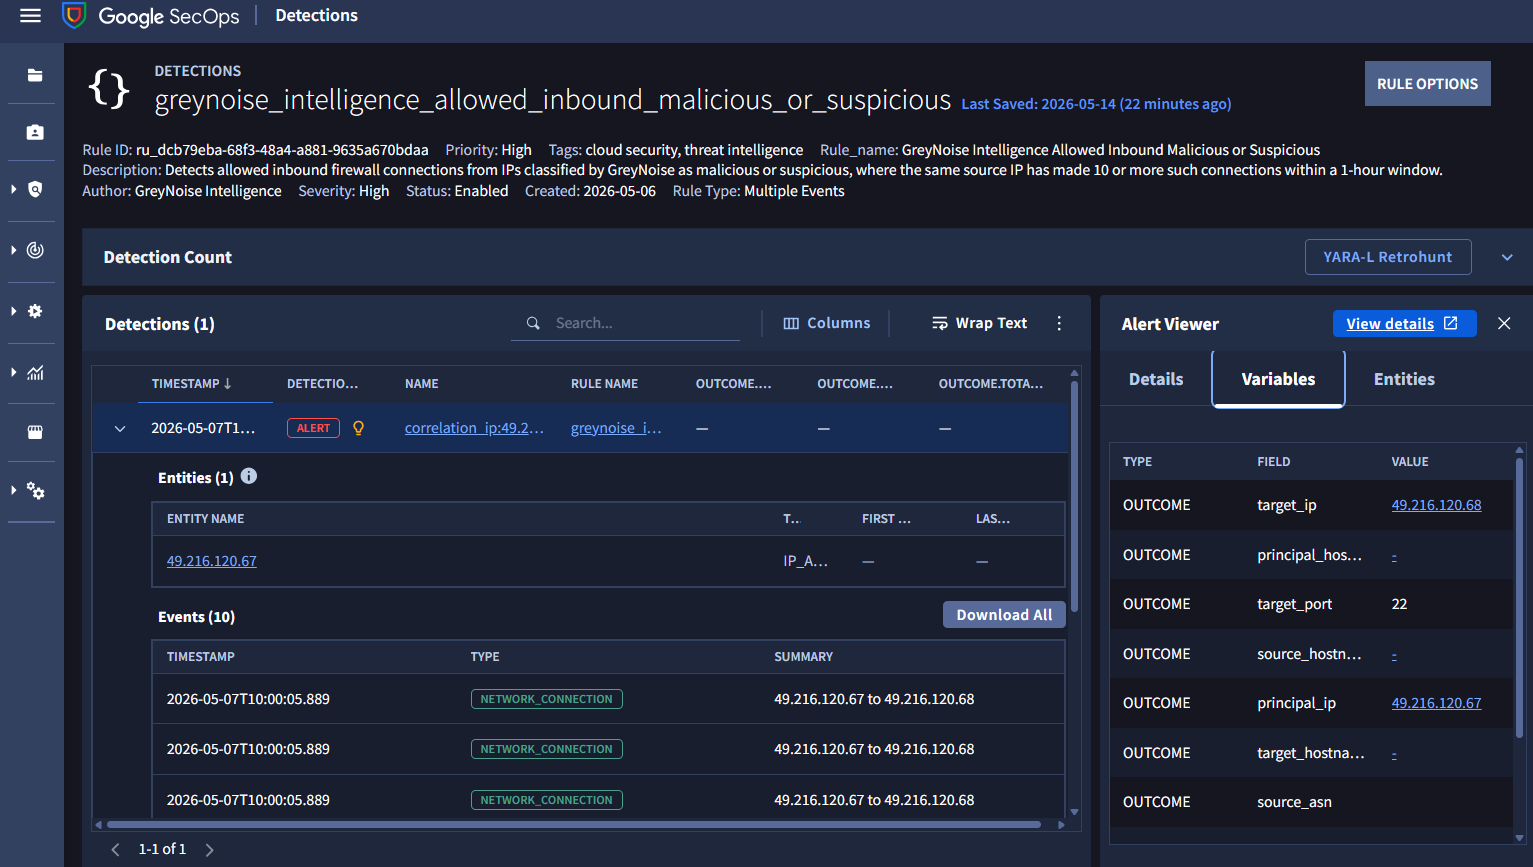
Misconfigured firewall rules, outdated access controls, and overly permissive policies can allow unauthorized traffic through the perimeter. Without external threat context, security teams may not recognize when a permitted connection originates from infrastructure associated with malicious activity.
Match allowed inbound traffic against GreyNoise intelligence in Google Security Operations SIEM. The YARA-L detection rule surfaces repeated connections from malicious or suspicious source IPs, giving analysts the context to investigate threats and identify potential gaps in perimeter controls.
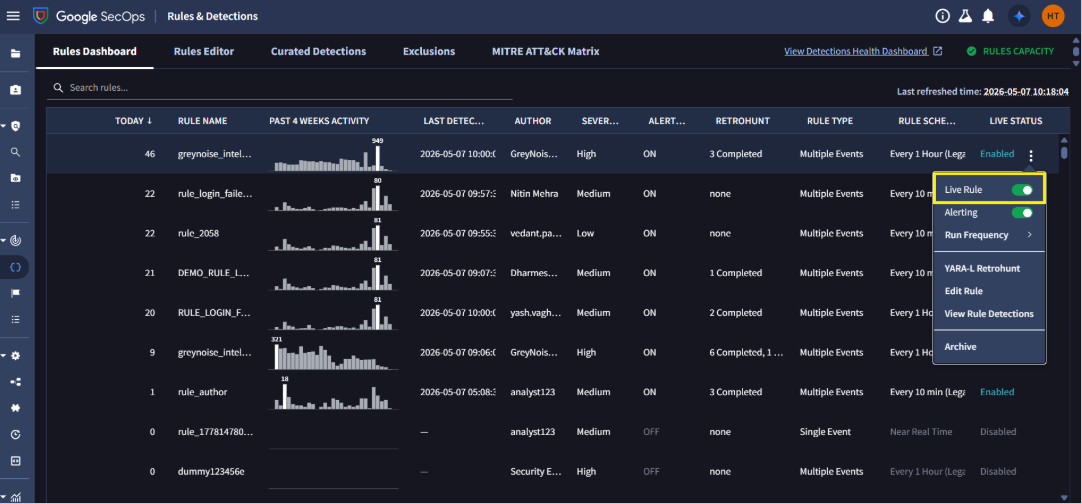
Internet-facing systems receive constant scanning, crawling, and opportunistic exploitation attempts that generate thousands of firewall alerts per day that are not real threats. This background noise can make real targeted attacks harder to identify and prioritize.
Google Security Operations SIEM correlates inbound events with GreyNoise observations to exclude known internet-wide scanning activity. What remains is a focused set of unknown IPs showing repeated activity against your environment, giving analysts stronger candidates for investigation.


